User Management
Each organization has its own users. This section covers creating users, inviting them, managing profiles and roles, and deprovisioning — through both the portal and the API.
User Lifecycle
Invited / Registered → Email Verified → Active → Blocked / Deleted
LumoAuth does not use a single status enum. A user's effective state is derived from a few flags: emailVerified, isActive, and isBlocked. The portal user list shows that state as the tags below:
| State | Description |
|---|---|
| Active | isActive = true and not blocked — can sign in |
| Inactive | isActive = false — account exists but cannot sign in |
| Blocked | Blocked by an administrator (isBlocked = true) — cannot sign in until unblocked |
| Deleted | Account removed (subject to GDPR retention) |
The emailVerified flag is tracked separately; an unverified user may still appear as Active depending on your verification policy.
Two kinds of account are created Inactive until the email is verified: self-service sign-ups, and accounts created by a social provider that did not verify the email. If the address is never verified, such a pending sign-up is deleted after 48 hours; an invitation to the same address can claim it earlier.
Managing Users
Portal
Navigate to Users in the sidebar (under Identity, /orgs/{orgId}/portal/users):
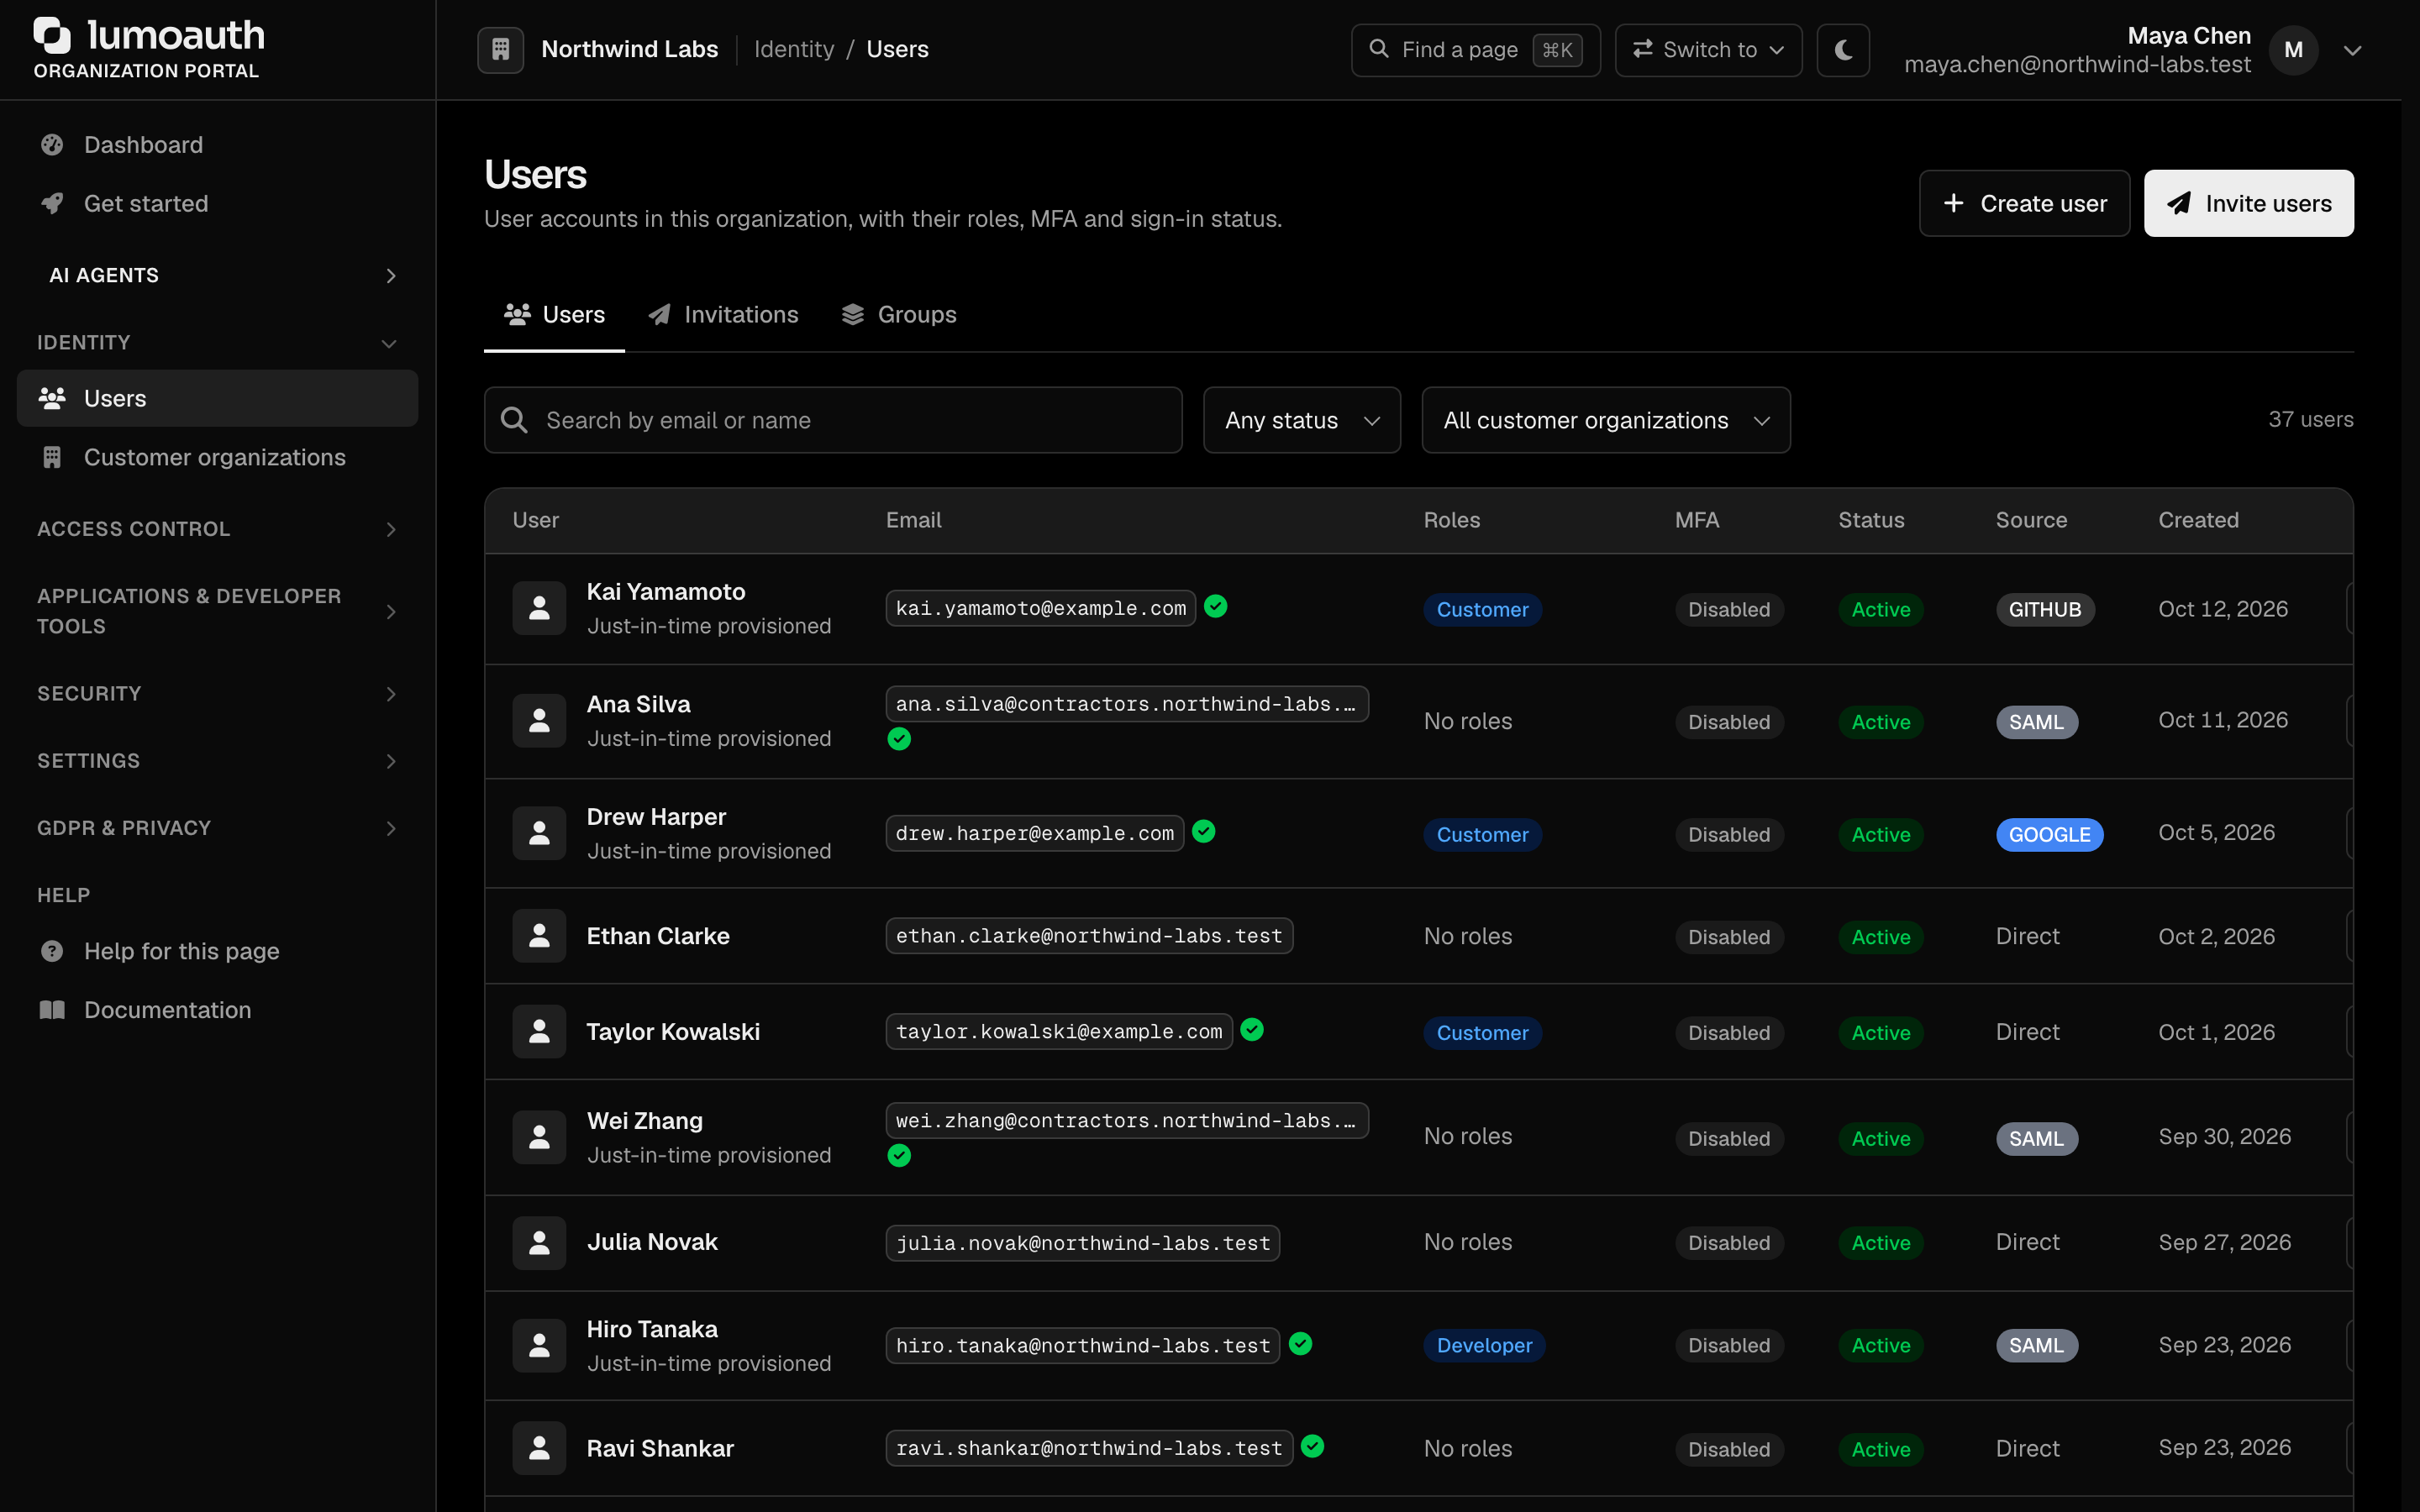
- User list - Search by email or name, filter by status or by customer organization, and browse all organization users. Each row shows the user's roles, MFA state, source and an Active / Inactive / Blocked tag
- Create user - Manually create a user account
- Invite users / Invitations - Send invitations and review the ones already sent
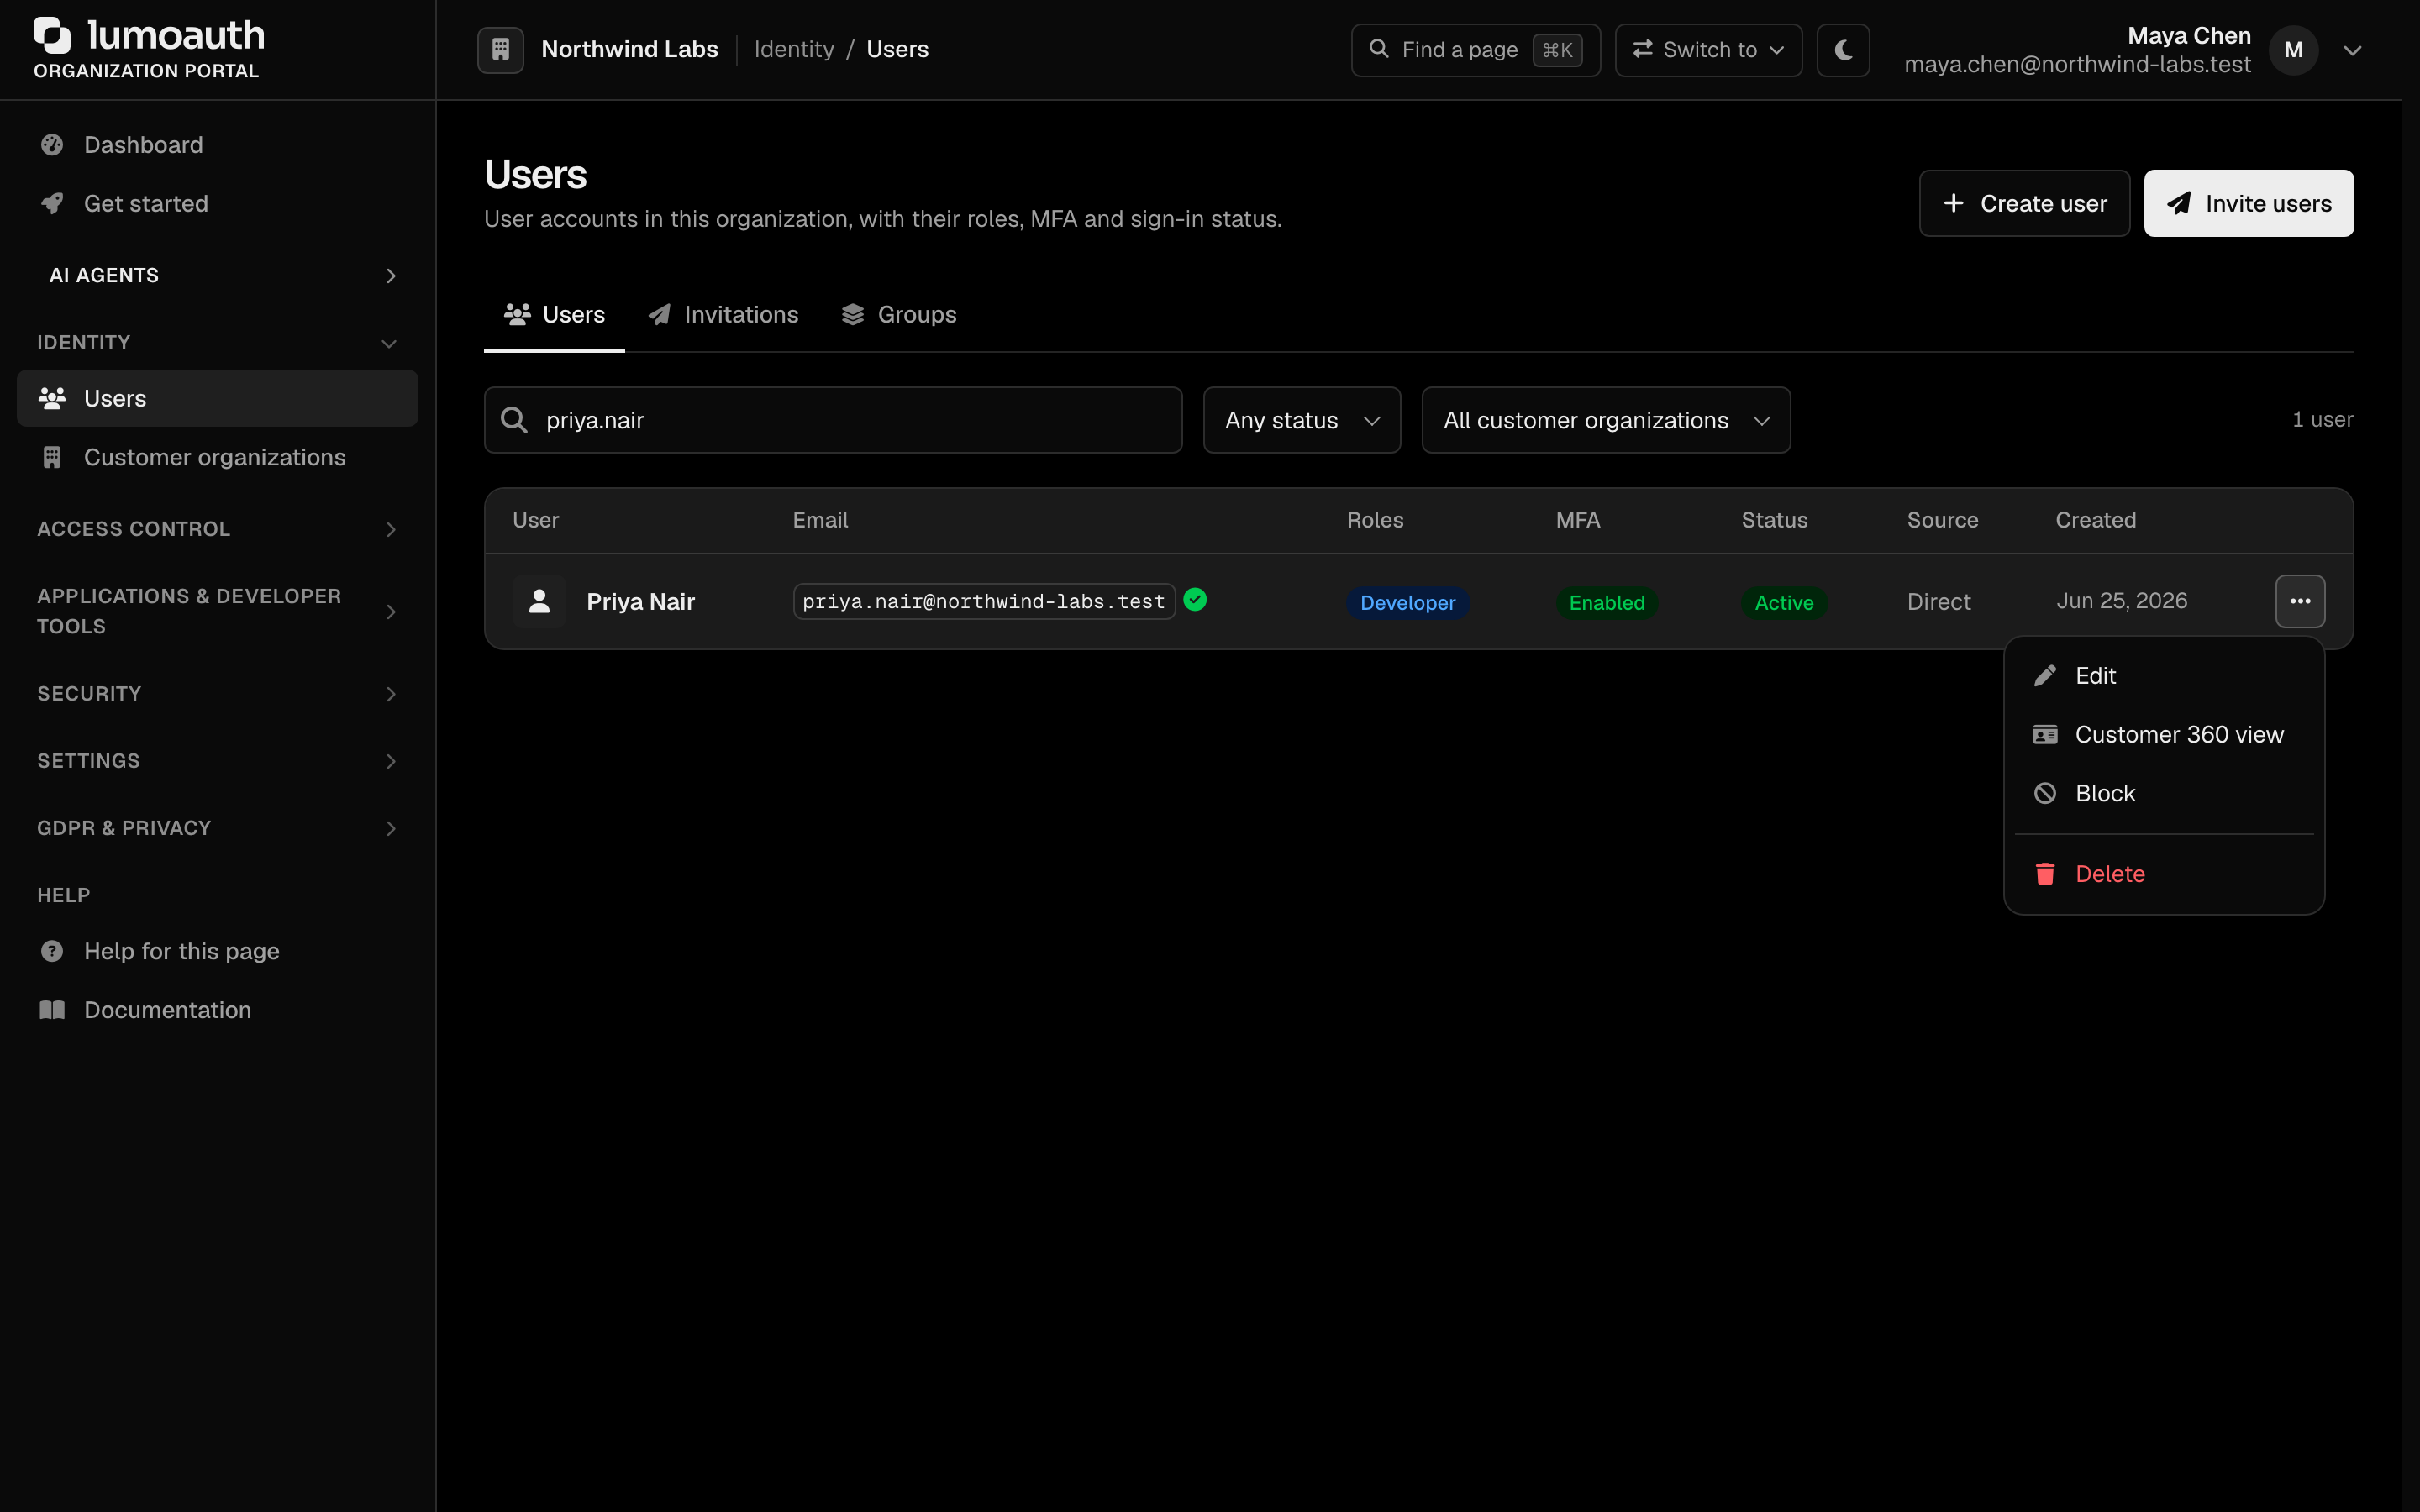
- Edit (from the ⋯ menu on a row) - Update profile fields, set a new password, manage roles and direct permissions, and switch Account active on or off. Under Two-step verification, remove a lost sign-in method or issue a temporary access code. Under Federated identities, link or unlink the user's SAML, LDAP or social identity. Group membership is managed from the Groups page
- Customer 360 view (from the ⋯ menu) - See Customer 360 View
- Block / Unblock (from the ⋯ menu) - Temporarily disable a user (Block) or restore access (Unblock)
- Delete (from the ⋯ menu) - Permanently remove a user
The ⋯ menu at the end of each row holds the per-user actions:
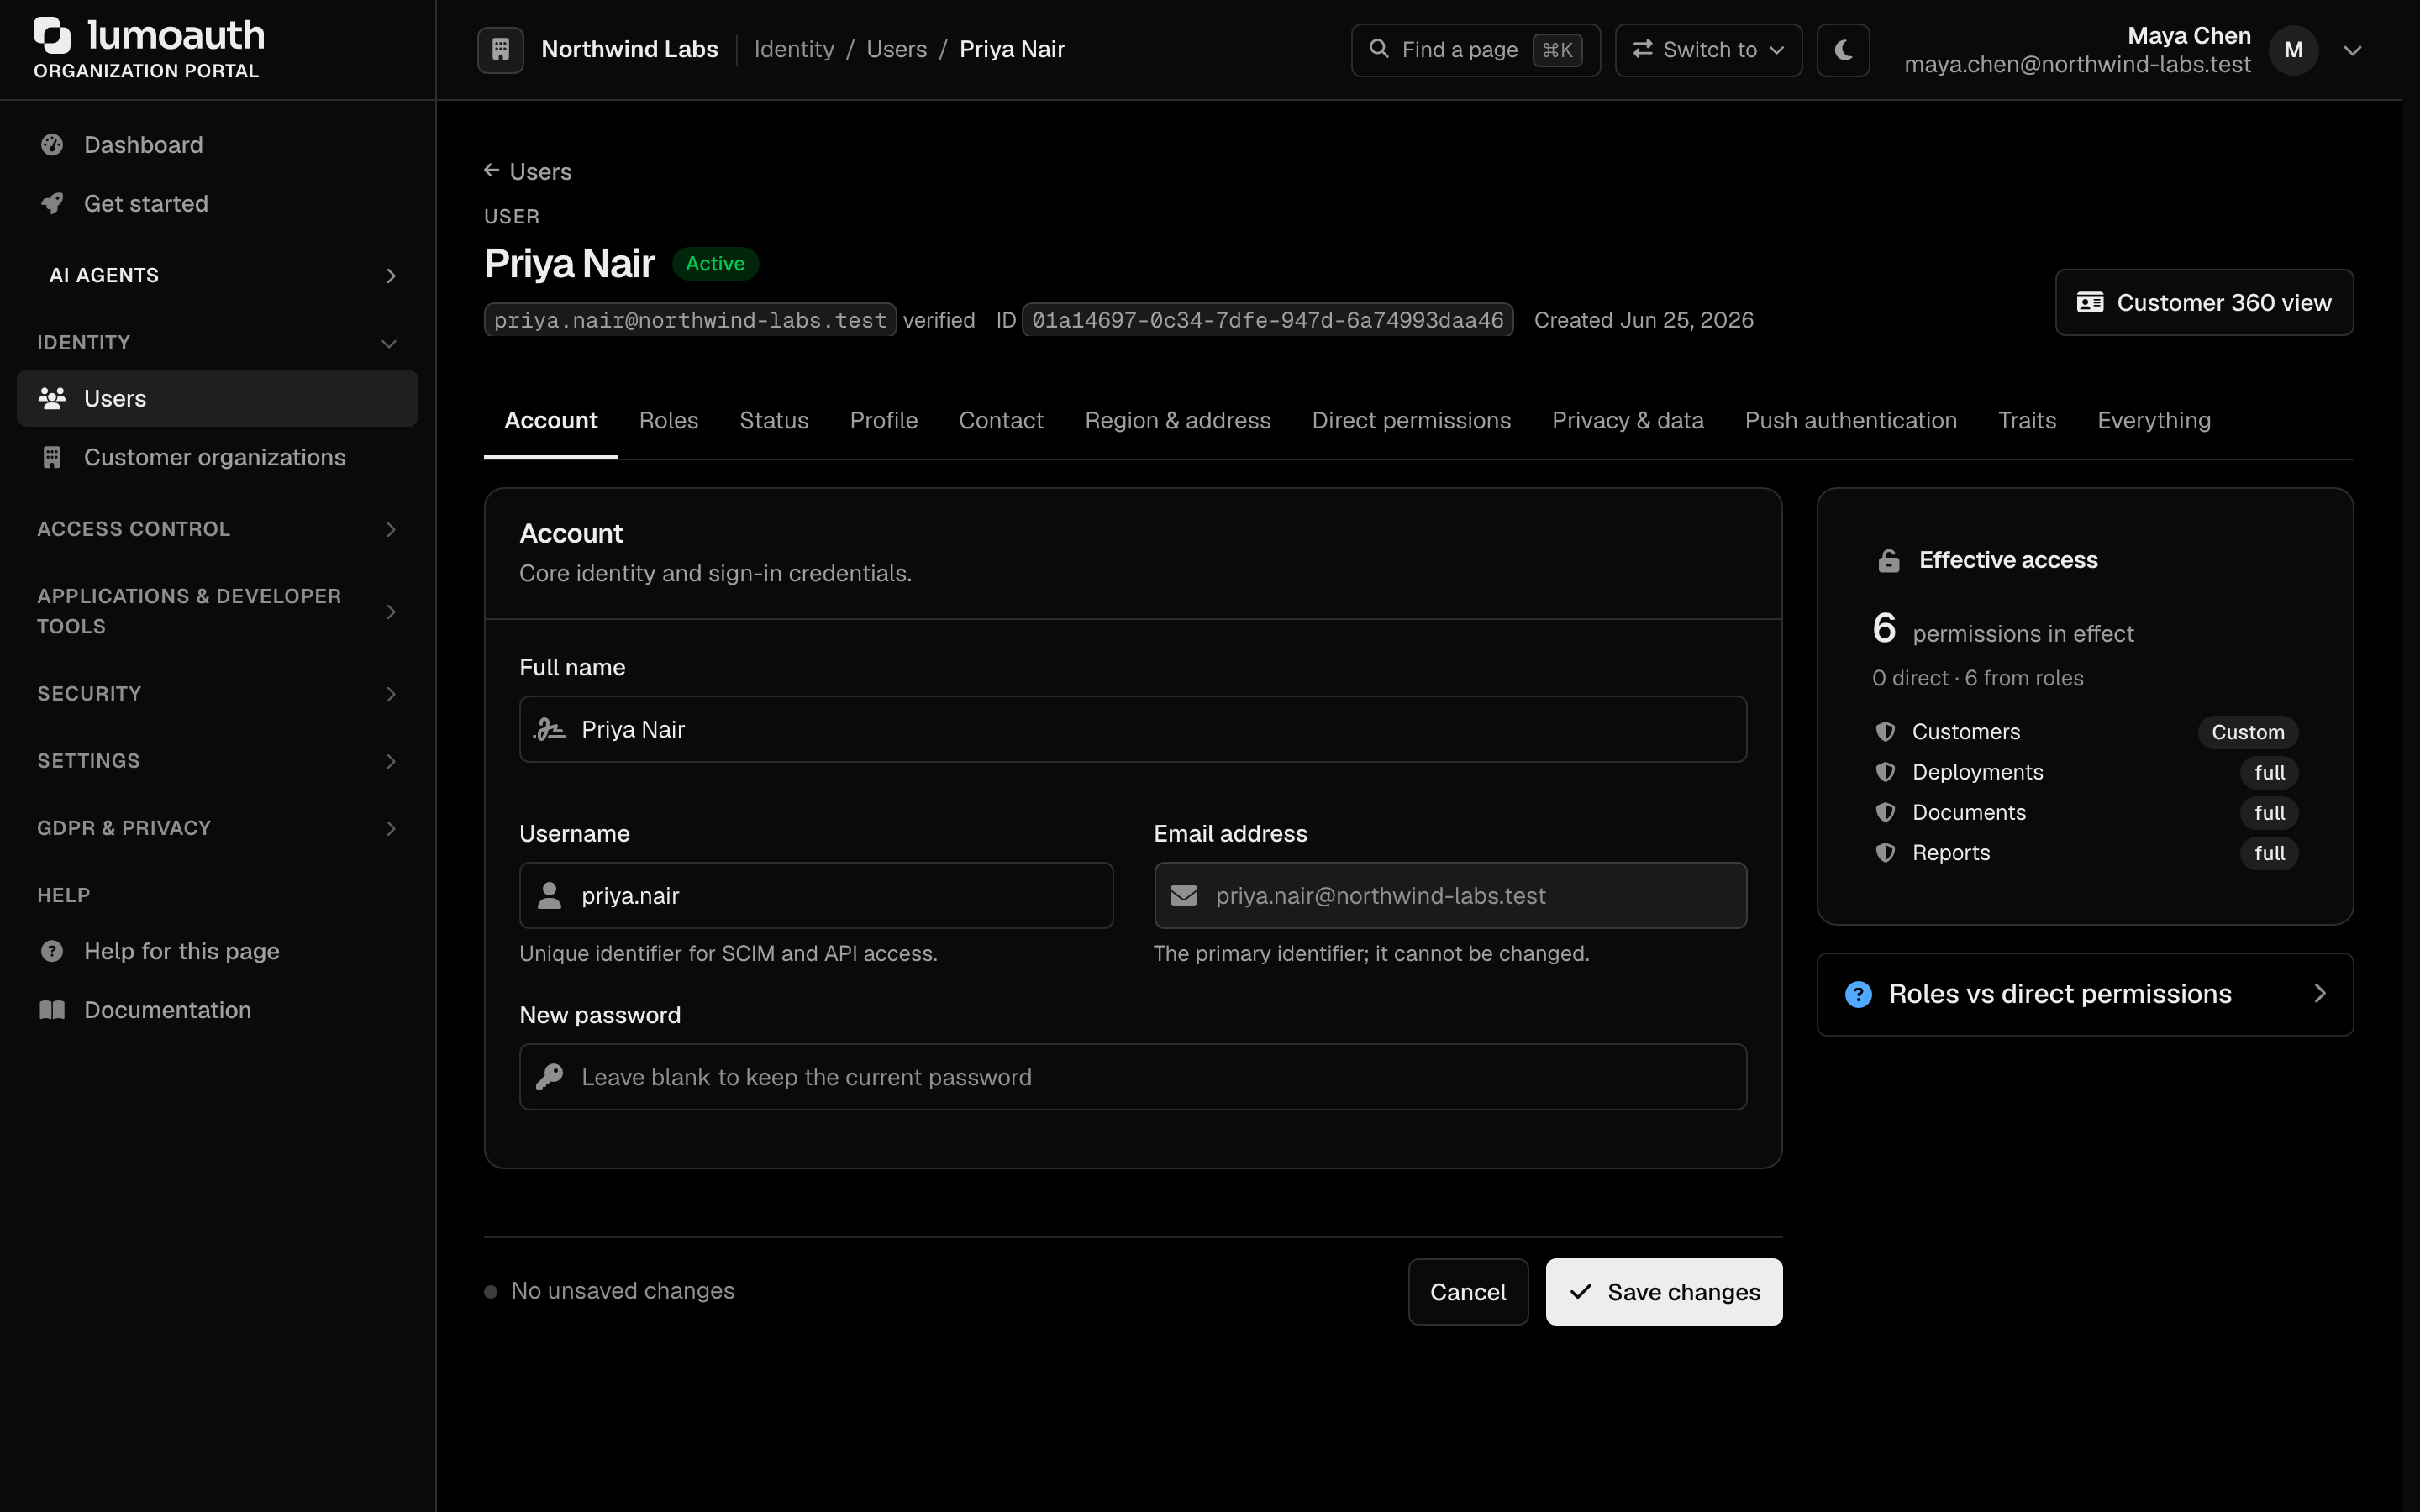
Edit opens the user's page, which is split into tabs: Account, Roles, Status, Profile, Contact, Region & address, Direct permissions, Privacy & data, Push authentication and Traits. Everything shows all sections on one page, including the Two-step verification and Federated identities cards:
User Profile Fields
| Field | Description | Editable |
|---|---|---|
| Primary identifier | Not by an admin in the portal (the field is read-only on the user's page); users change it themselves from Personal info | |
| First Name | Given name | Yes |
| Last Name | Family name | Yes |
| Phone | Profile phone number (text-message MFA uses the number that the user verified during MFA enrollment, not this field) | Yes |
| Email Verified | Verification status | Admin only |
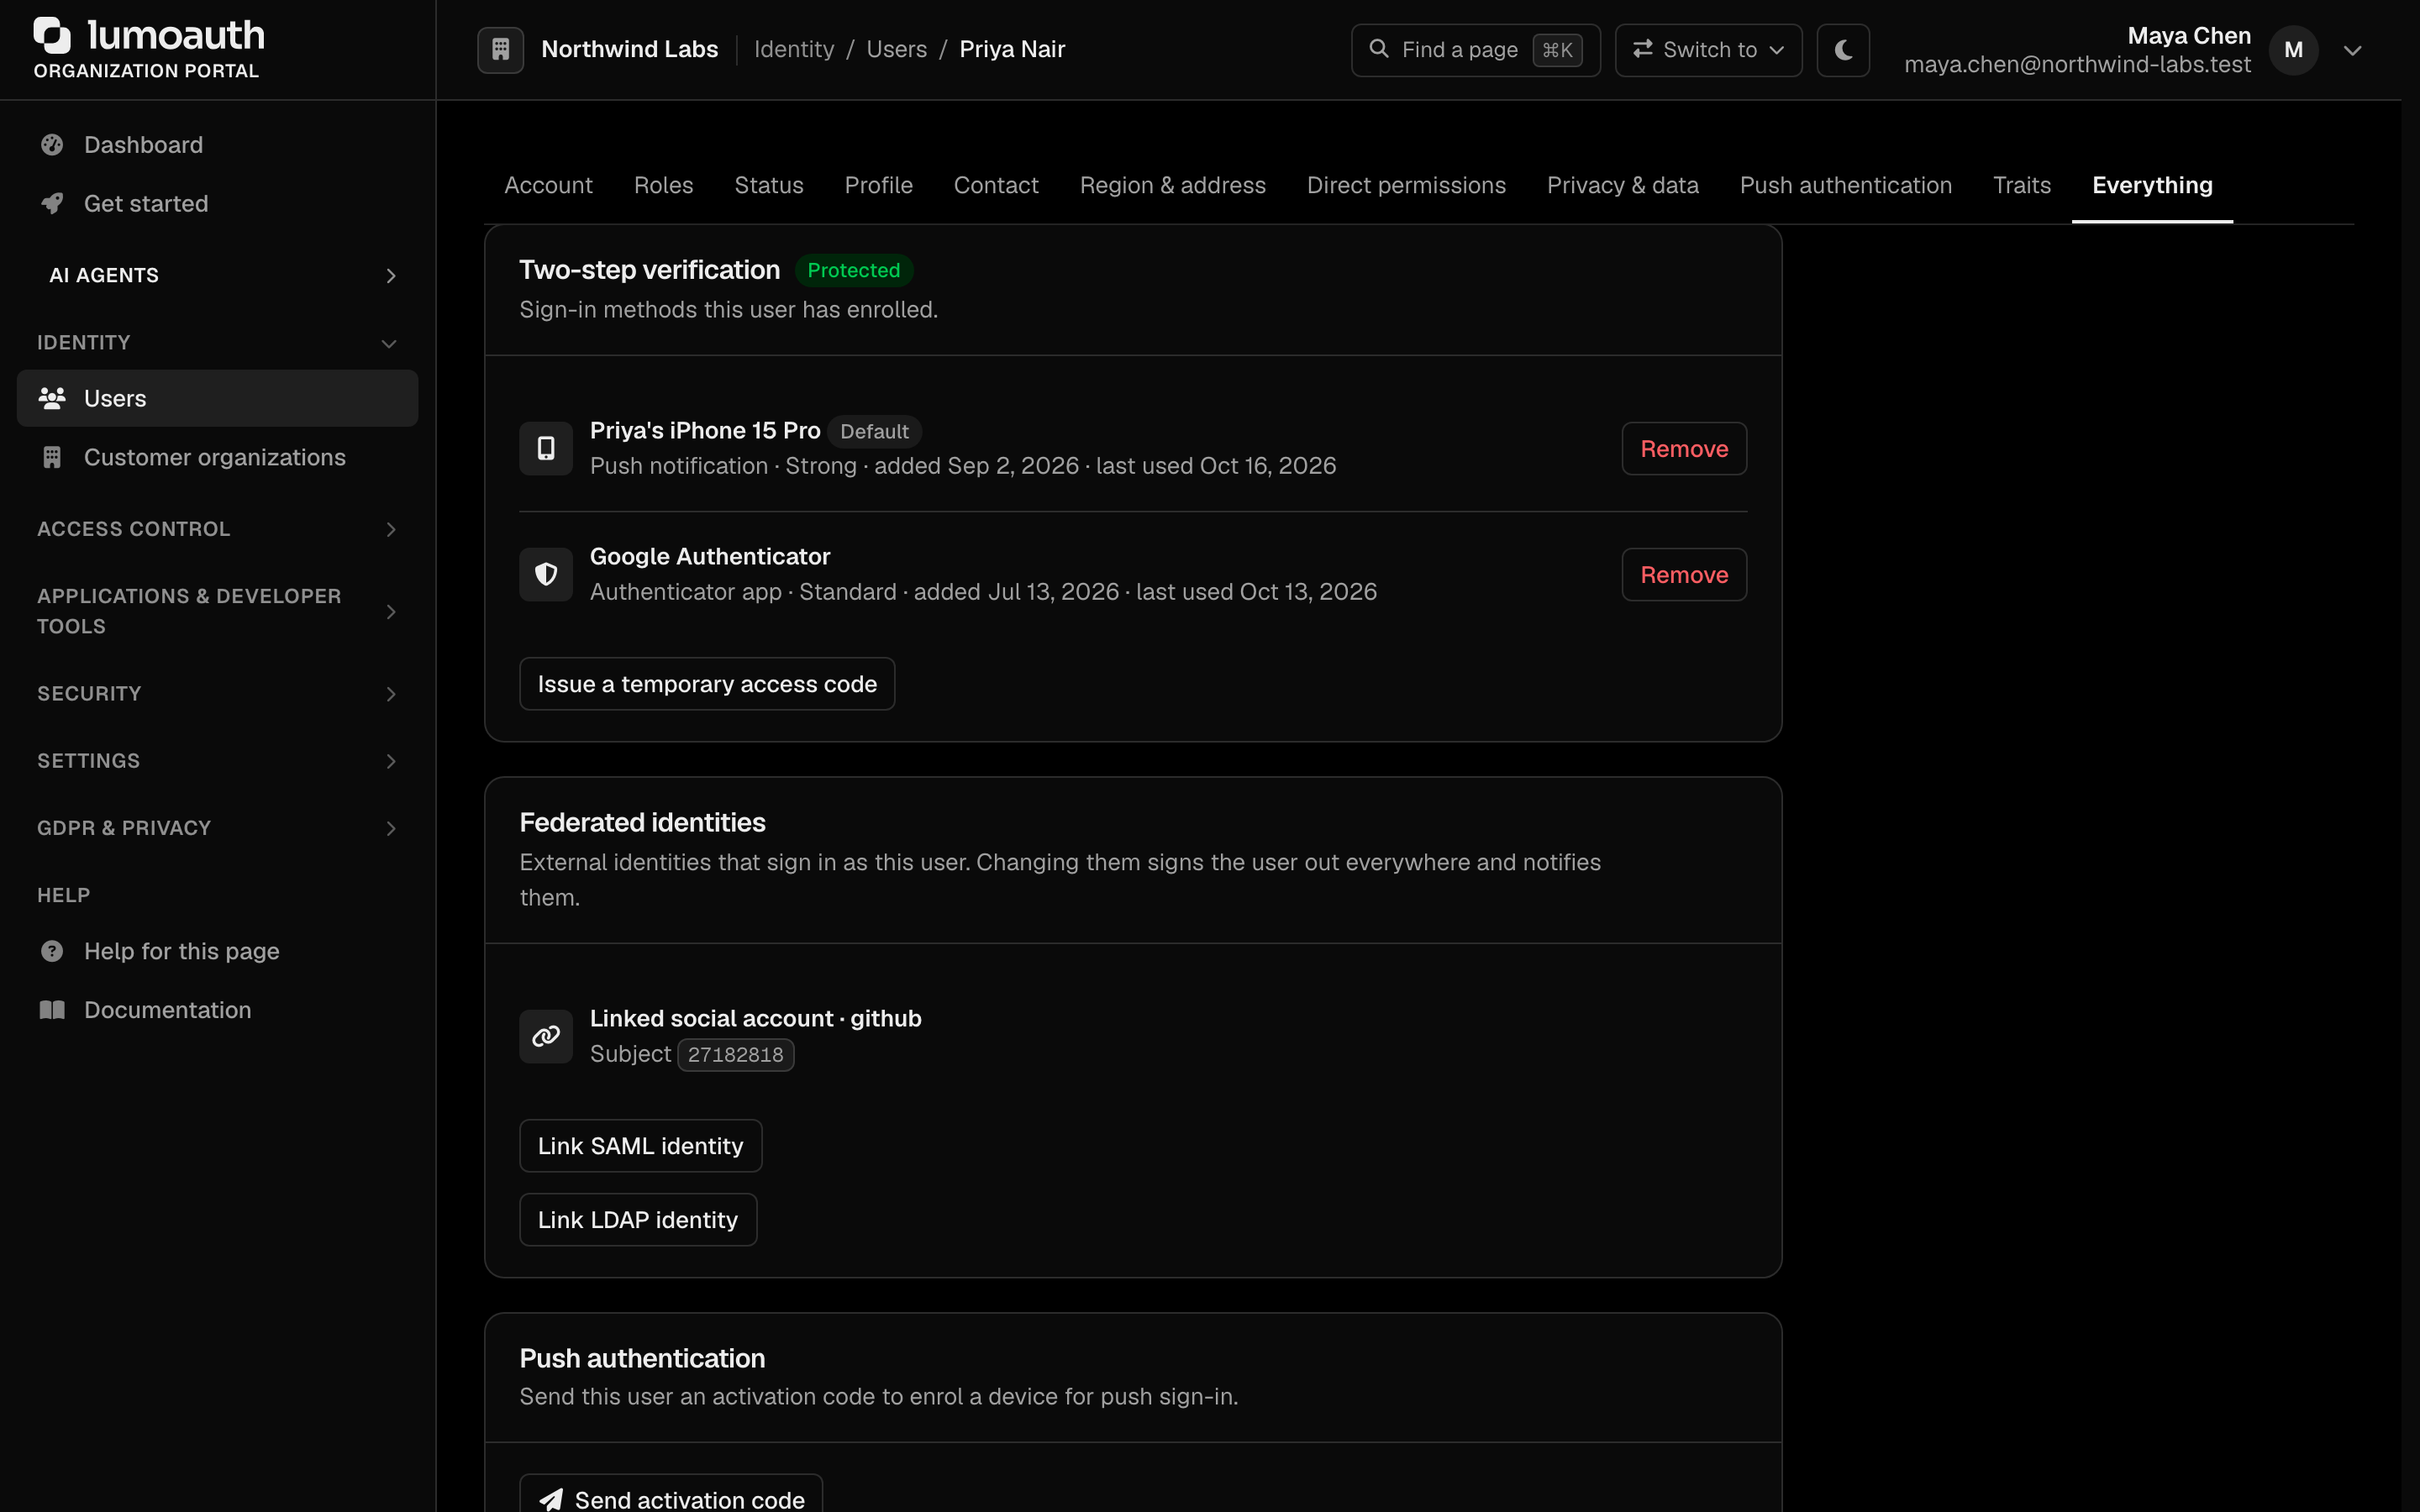
| Two-step verification | The user's enrolled sign-in methods. Admins can Remove one or Issue a temporary access code, but cannot turn MFA off; who must use MFA is set by the organization's MFA policy | Admin actions only |
| Federated identities | The SAML IdP + NameID, LDAP directory + DN and social provider linked to the account. Admins can Link SAML identity, Link LDAP identity or Unlink; each change signs the user out and emails them. See Relinking federated identities | Admin actions only |
| Roles | Assigned roles | Admin only |
| Groups | Group memberships (managed from the Groups page) | Admin only |
| Created At | Account creation timestamp | No |
| Last Login | Most recent authentication | No |
The Two-step verification and Federated identities cards are shown on the Everything tab of the user's edit page (?section=all), above Push authentication:
Creating Users
Manual Creation
- Go to
/orgs/{orgId}/portal/users - Click Create user
- Enter the Full name, Email address and an initial Password. The password is required here and must meet the organization's password policy and breached-password check. The Admin API
POST /admin/usersmay omit it; when given, the same checks apply - Leave Active on to let the user sign in as soon as the account is created
- Optionally select Roles, and fill in the optional Contact and profile and Region and address sections
- Click Create user
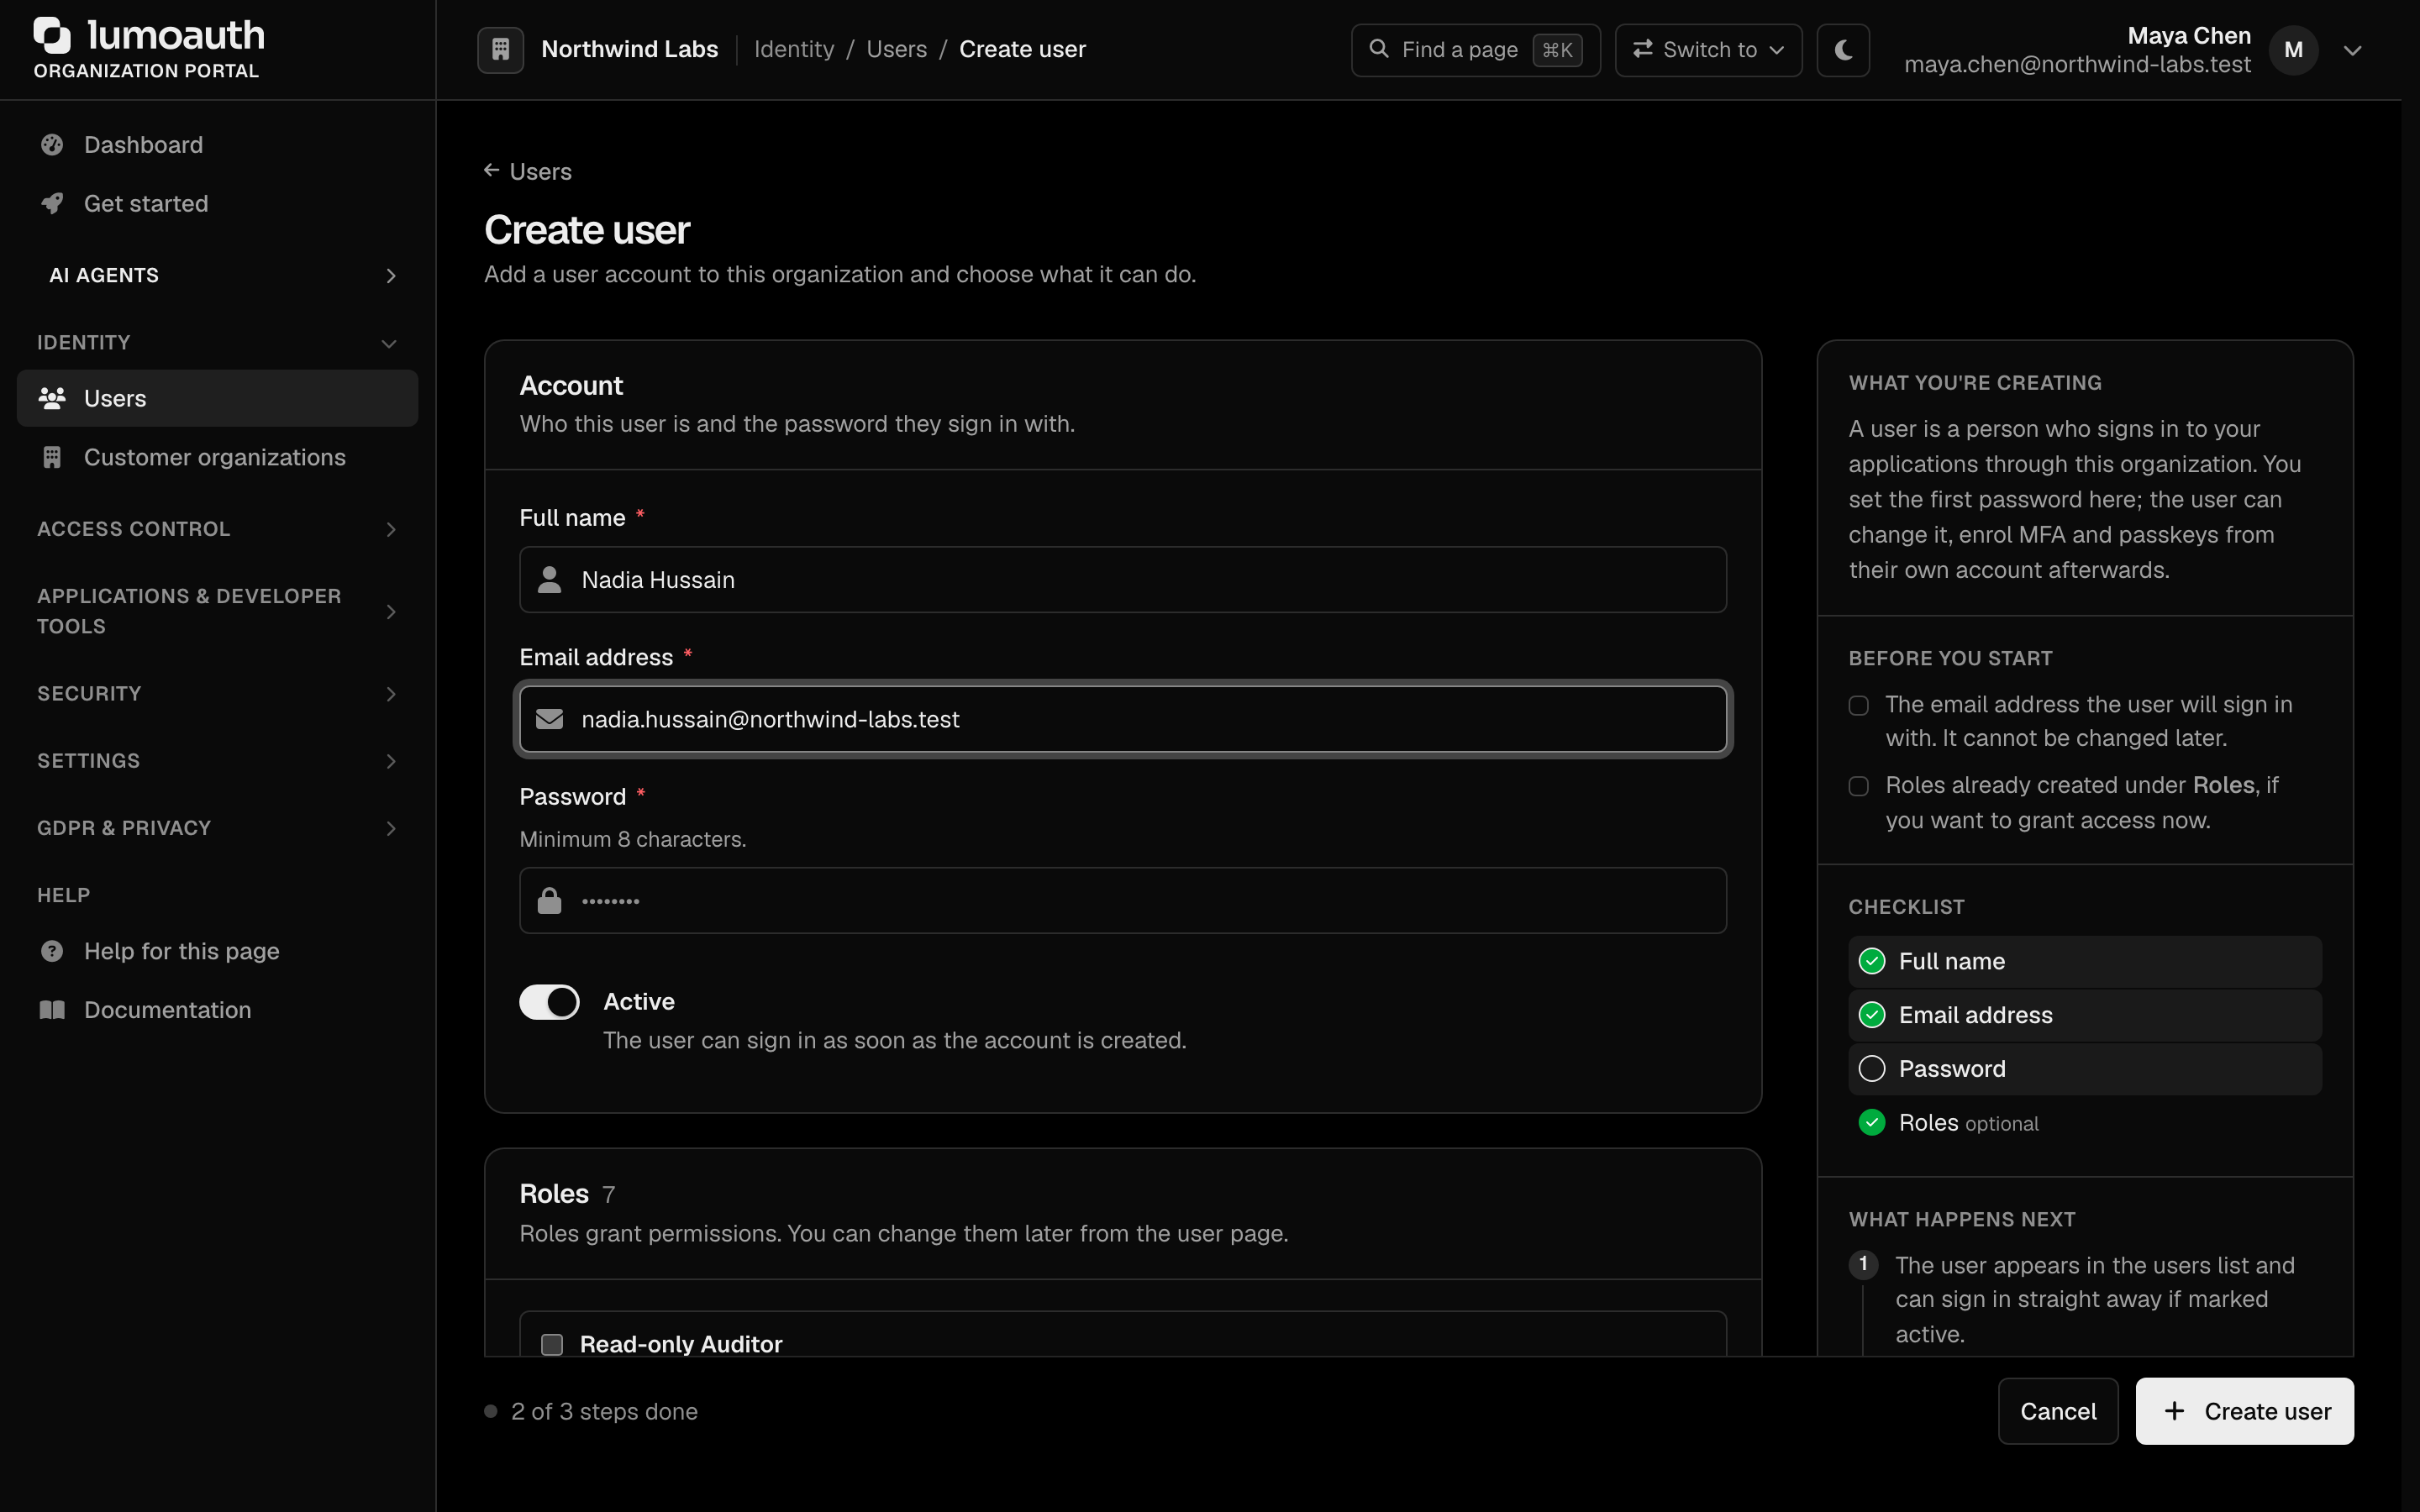
The page does not send a welcome email and does not assign groups; pass the password to the user yourself, or use an invitation so that they choose their own. Add the user to groups afterwards from the Groups page.
Self-Registration
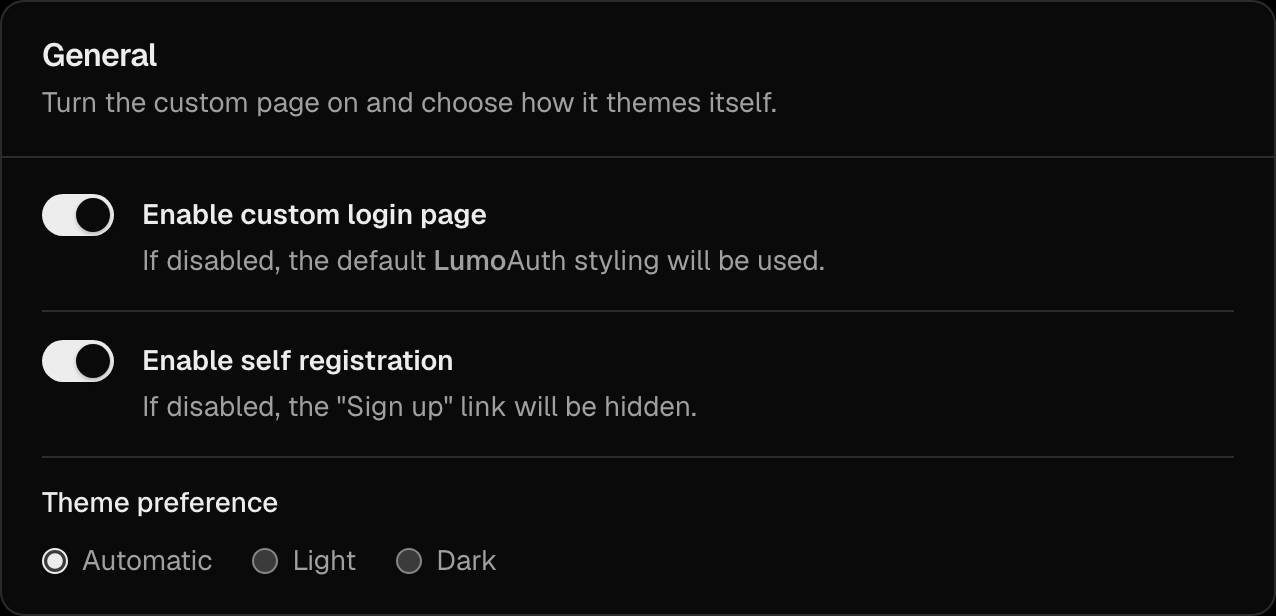
Users can register themselves from the organization's login page if the Enable self registration toggle is on. The toggle is in the General section of the Login page settings (/orgs/{orgId}/portal/settings/login-page). Turn it off to require invitations.
SCIM Provisioning
Users can be provisioned automatically from external identity providers using SCIM 2.0.
JIT Provisioning
When a user signs in via Social Login, SAML, or OIDC Federation for the first time, their account is created automatically. This is just-in-time provisioning: the account appears at first sign-in instead of being created in advance.
Customer 360 View
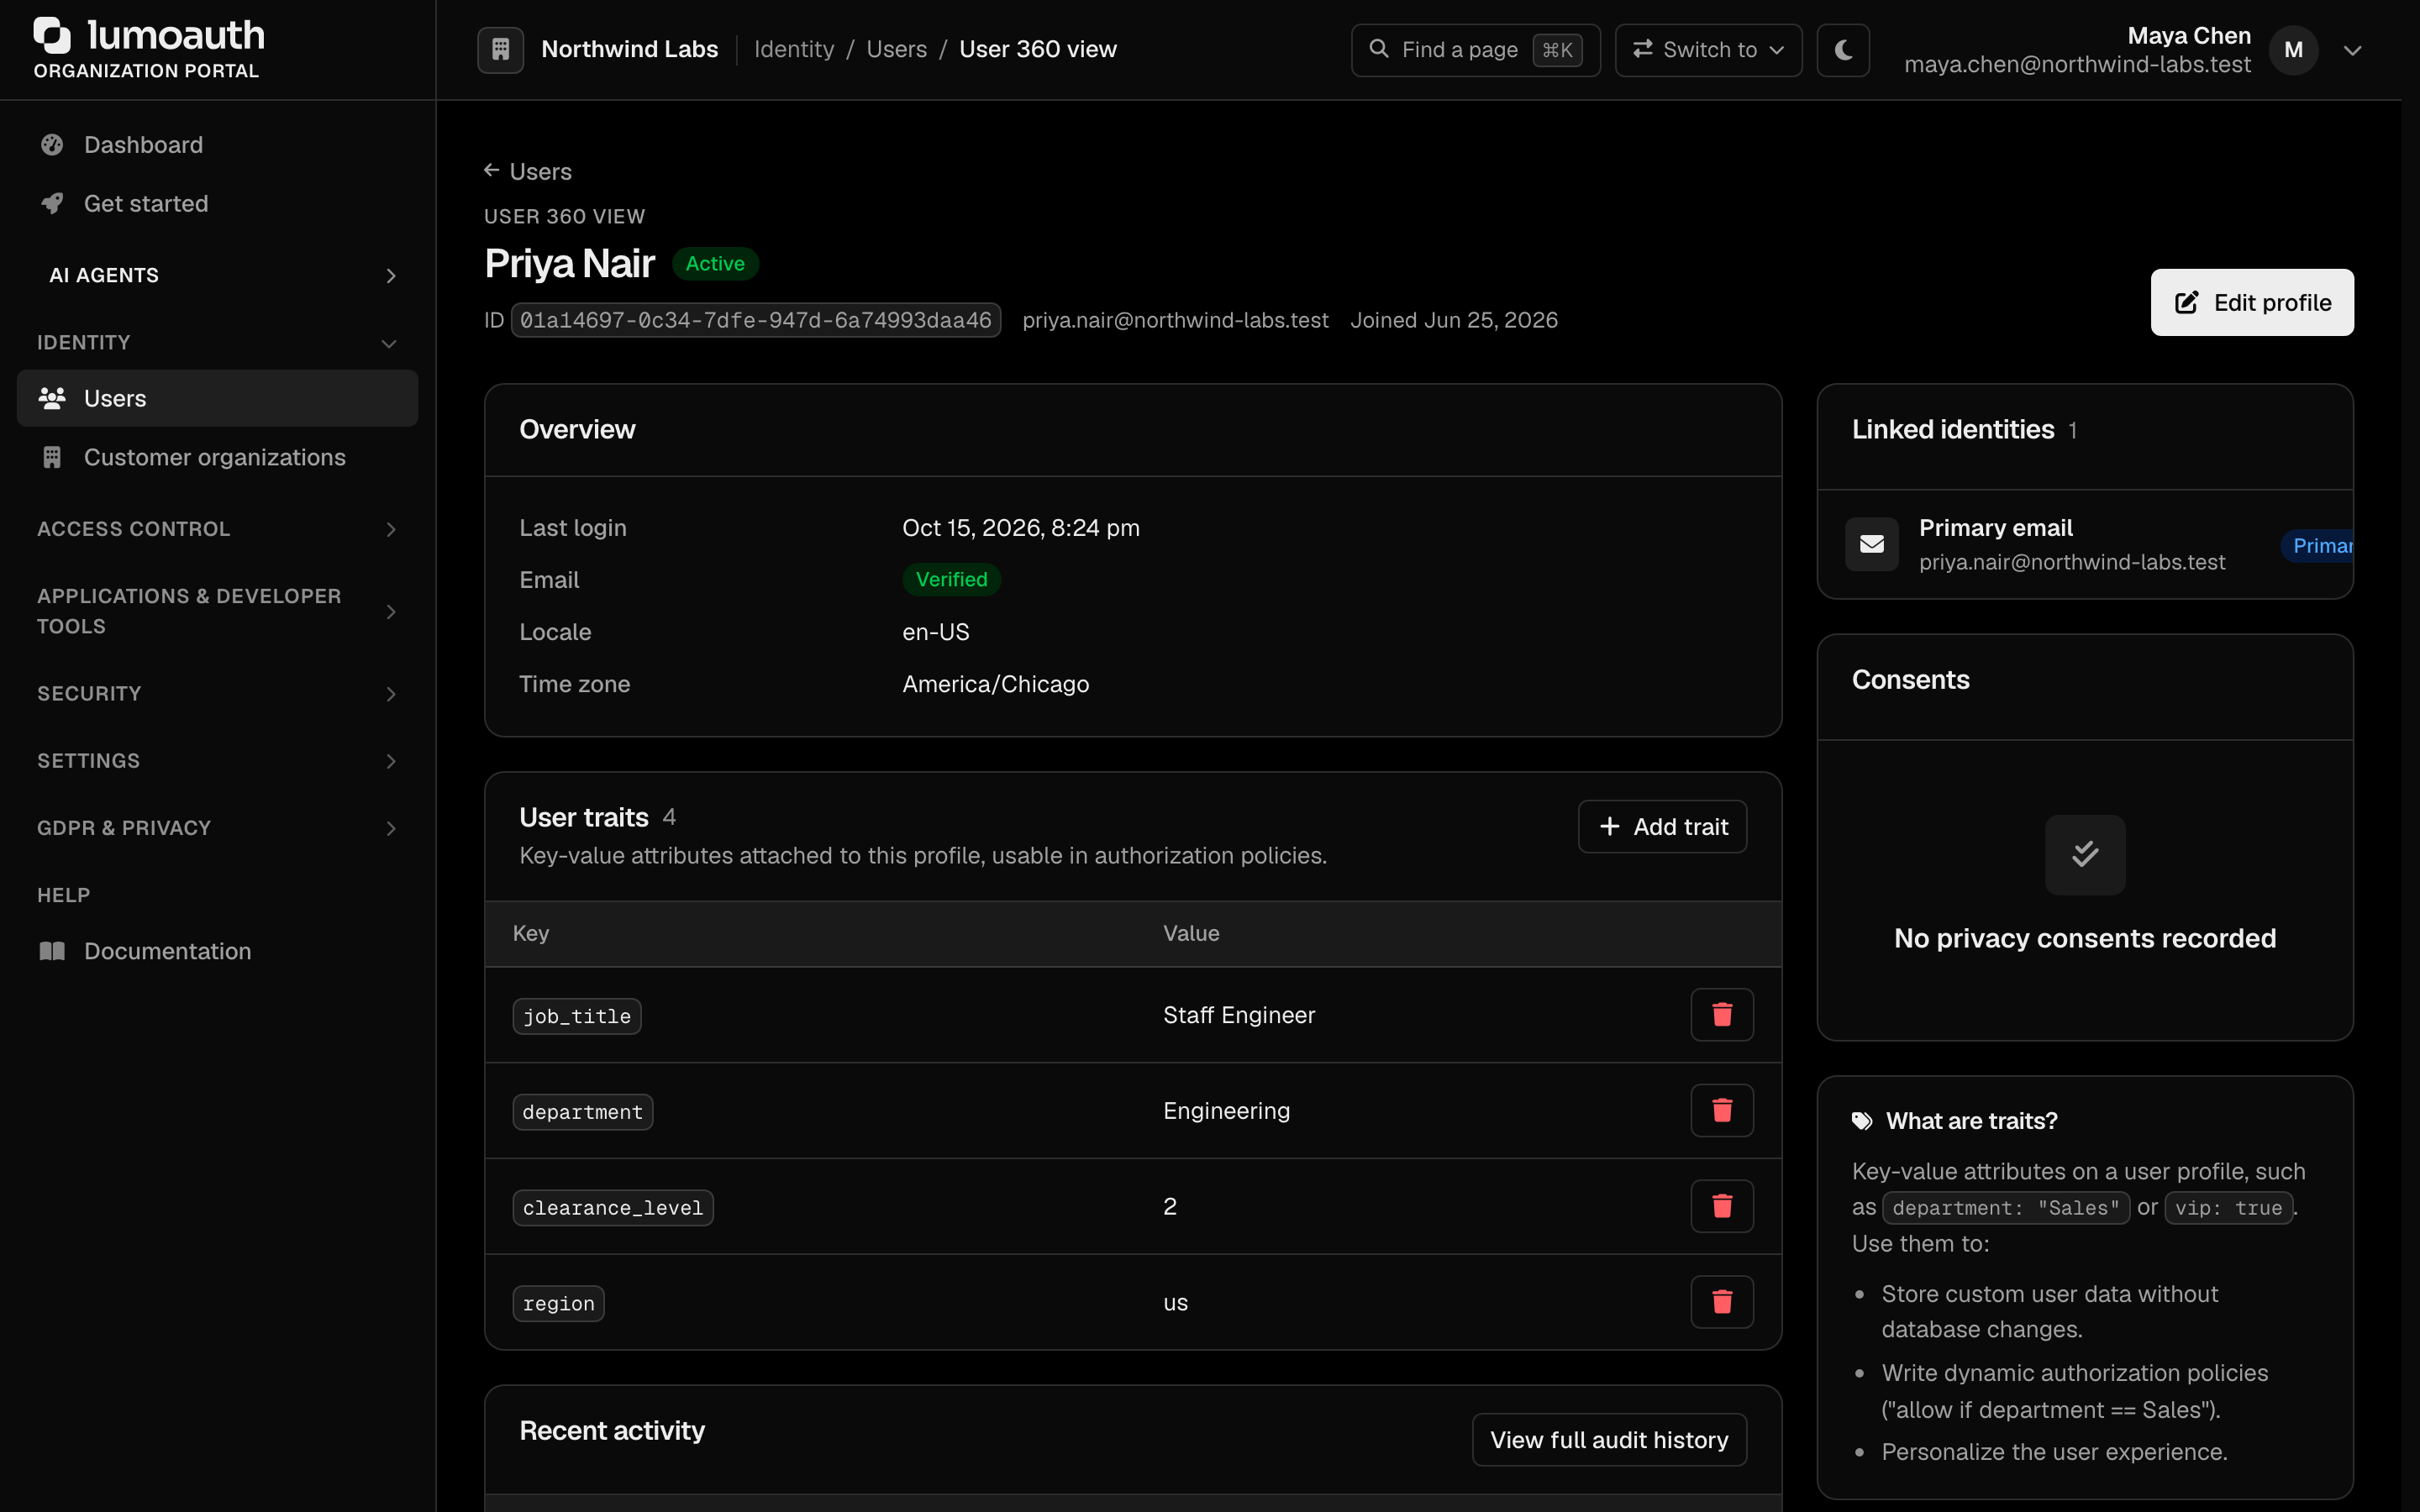
Each user has a Customer 360 page (titled User 360 view) that brings together everything about them in one place:
- Overview — last login, whether the email is verified, locale and time zone
- Linked identities — connected social accounts, SAML, and OIDC logins
- User traits — custom key-value attributes (string, number, boolean, JSON)
- Consents — what the user has consented to, with dates
- Recent activity — the 20 most recent audit events for this user, with a View full audit history link
Open it with Customer 360 view in a user's ⋯ menu on the Users page or on the user's edit page, or go to /orgs/{orgId}/portal/users/{userId}/360.
User Traits
User traits are custom attributes that you can attach to any user to store application-specific data. Traits can be edited from the Customer 360 view and can be used in ABAC policies for attribute-based authorization decisions.
See Progressive Profiling & User Traits for full details.
Progressive Profiling
Progressive profiling lets you collect user information gradually during the login flow. It asks for one or two fields per session rather than a long upfront form. Configure profiling rules in the Progressive profiling section of Sign-in settings.
See Progressive Profiling & User Traits for full details.
Customer organizations
Users can belong to one or more customer organizations within your organization (Identity → Customer organizations). They model the companies, teams or workspaces that your product serves, each with its own members and member roles.
See Customer organizations for full details.
In This Section
| Guide | Description |
|---|---|
| Invitations | Invite users to join your organization |
| Sessions | Manage user sessions and tokens |
| Account Self-Service | Password reset, profile updates, MFA enrollment |
| Customer organizations | The companies and teams that your product serves, with their own members and roles |
| Progressive Profiling & User Traits | Gradual data collection and custom user attributes |