AI Agents Track
Use this track when you are building an agent that operates on its own, chains tool calls, or acts on a user's behalf. OAuth alone was not designed for this — you need an identity for the agent itself, not just the user. By the end of this track you will have a registered agent, scoped capabilities, and just-in-time approval connected.
Do the AI Agent + MCP in 5 Minutes quickstart — the flagship path, in the sidebar under Quickstarts → AI Agents. Prefer the mental model first? Read How LumoAuth secures an agent, or watch the same flow in the interactive demo (simulated, no signup).
Prerequisites
- A LumoAuth organization — sign up; agent identity (AAuth) is available on every plan, nothing to switch on
- Node.js 18+ or Python 3.9+
1. Understand why this matters
Read Why AI Access Control. Key ideas:
- Agent Registration — every agent is a first-class identity, not a shared API key
- Scoped Capabilities — agents request specific capabilities (
document.read,payments.authorize), not a blanket "admin" role - Chain of Agency — token exchange (swapping one token for another that records who asked whom) encodes the full call chain: "Tool → Agent → User"
- JIT Permissions — human approval in the loop for sensitive operations
2. Register your agent
Follow the AAuth Quick Start — register an agent, generate an Ed25519 key pair, and get your first access token. Ed25519 is a modern public-key signature algorithm; it is fast and produces short keys. The wire format is pinned in the AAuth 1.0 protocol spec.
3. Pick your framework
| Framework | Registry | JIT |
|---|---|---|
| LangChain / LangGraph | Registry | JIT |
| CrewAI | Registry | JIT |
| OpenAI Agents SDK | Registry | JIT |
| Agno | Registry | JIT |
| Google ADK | Registry | JIT |
| Microsoft Agent Framework | Registry | — |
4. Authorize agent actions
- Ask API — natural-language permission checks, intended for reasoning loops in an LLM
- Fine-grained authorization — the
/authz/checkfamily answering for agent subjects (ReBAC + ABAC + RBAC) - JIT Permissions — request human approval before running a sensitive operation
- Chain of Agency — used when the agent acts on a user's behalf; built on token exchange
- Cross-app access — an agent authenticated in one app reaching a resource in another, without a second sign-in, via the identity-assertion grant (ID-JAG)
- Token vault — store and mint delegated credentials for the third-party APIs that an agent calls
5. Approvals in the loop
Sensitive actions pause for a human before they run. Before you test this, make sure somebody can approve:
- The reviewer needs the
jit.approvepermission. Organization admins hold it by default; for other people, create a role that grants onlyjit.approve(how). - The reviewer must not be the owner of the agent, and must not be the user that the agent acts on behalf of. If you registered the agent yourself, you need a second person (or a sandbox organization) to approve its requests.
- Decide from the portal inbox (
/orgs/{orgId}/portal/approvals), a phone, or a chat or ticketing tool. The rules are the same everywhere; see JIT review rules.
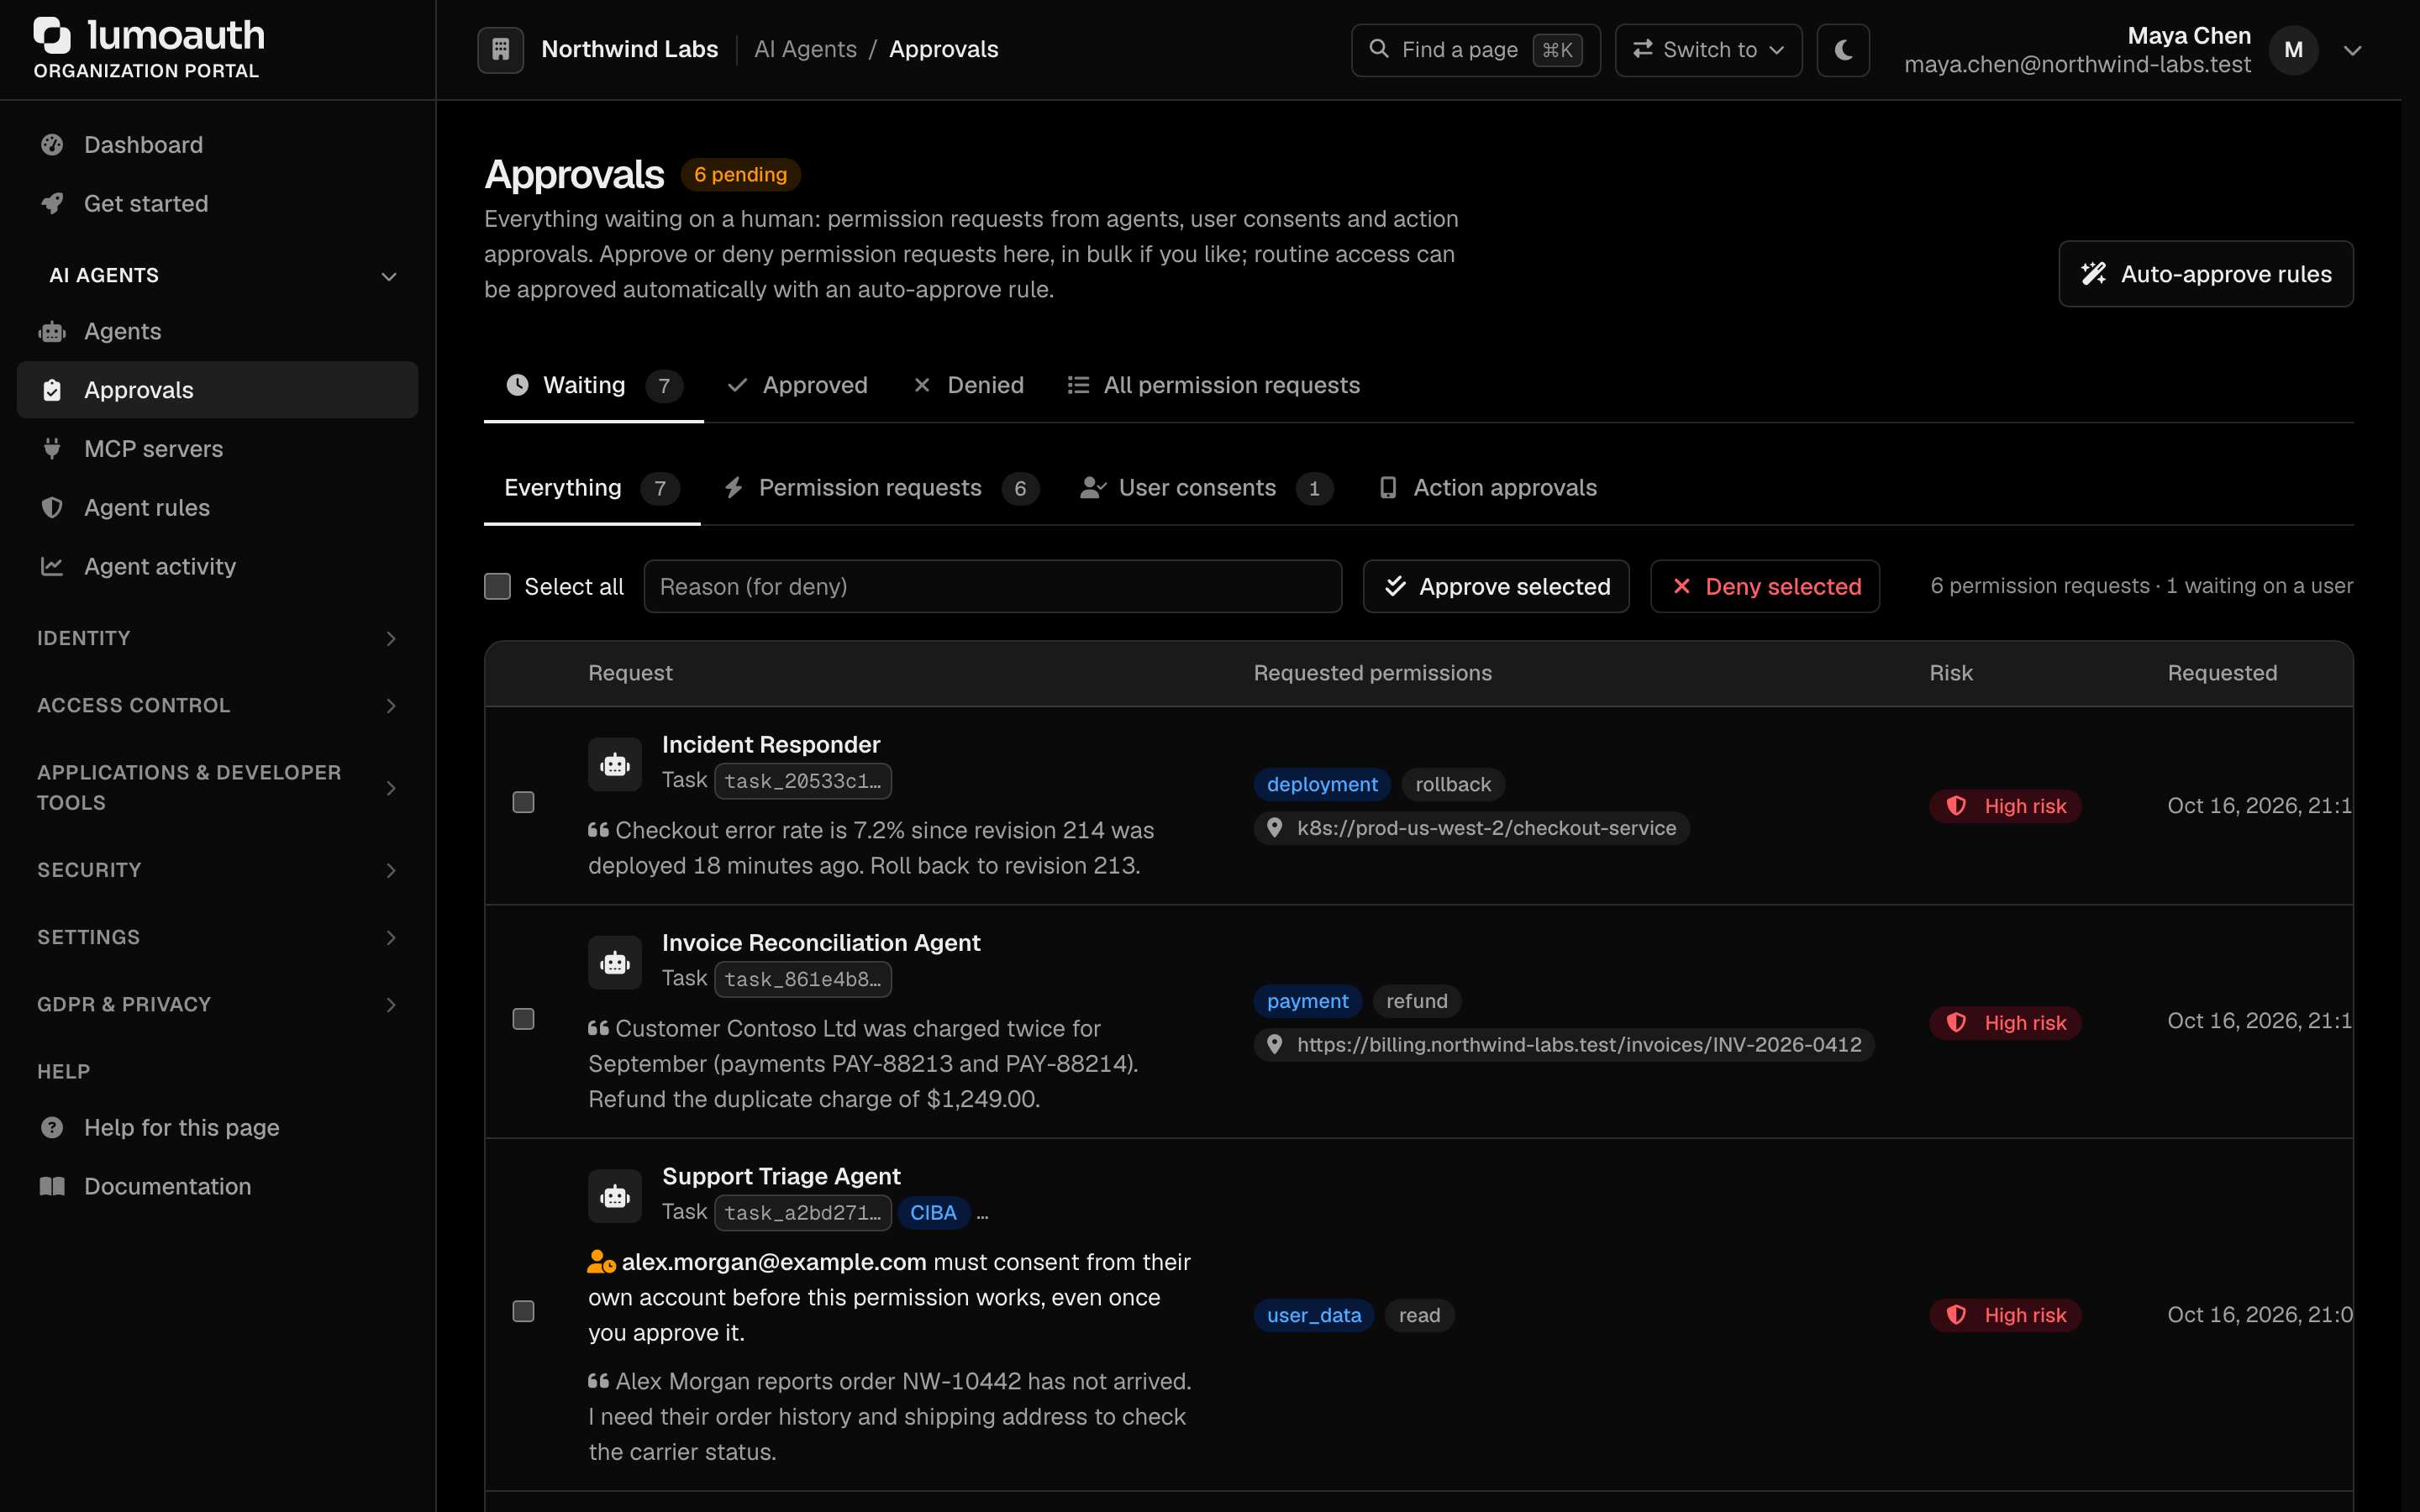
- Async authorization — backchannel (CIBA-style) approval on the user's own device, connected to JIT, with a live-updating approvals inbox
- Push approval and mobile approvals — approve or deny agent requests from a phone
- Approval channels — Slack, Microsoft Teams, ServiceNow and Jira Service Management
6. Advanced
- AAuth Protocol — cryptographic agent identity using signed HTTP requests (every request carries a signature made with the agent's private key)
- Attestation — attestation-based client authentication and verification of SPIFFE workload-identity tokens (JWT-SVID), so an agent proves where it runs
- Workload Federation — use the platform's own workload identity (Kubernetes, AWS, GCP) so the agent never needs a static secret
- Governance — risk scoring, conditional-access rules (created with Create rule on the Access rules tab under Agent rules), the kill switch, and dormancy lifecycle for your agent fleet
- Shared signals — a shared-signals (SSF/CAEP) transmitter that pushes security events about agents, such as a revoked session, to the apps that rely on them
- MCP Servers — authorize Model Context Protocol tool calls
Next track
- Building the backend that the agent calls? → Backend / Service Track
- Operating at scale? → Security & Compliance Track
Standards used on this page
| Plain name | Standard |
|---|---|
| Token exchange (delegation) | RFC 8693 |
| Cross App Access (identity assertion JWT authorization grant, ID-JAG) | Identity Assertion Authorization Grant (draft) |
| Client-initiated backchannel authentication (CIBA) | OpenID CIBA Core 1.0 |
| Signed HTTP requests (HTTP message signatures) | RFC 9421 |
| Shared Signals Framework (SSF) and Continuous Access Evaluation Profile (CAEP) | OpenID SSF 1.0, OpenID CAEP 1.0 |
See the standards reference for what each one covers and how LumoAuth uses it.