Organization Setup
This guide covers configuring and managing your organization in LumoAuth.
Getting Your Organization
When you sign up for LumoAuth, you create an organization during onboarding. Your organization is immediately available at:
https://app.lumoauth.dev/orgs/{your-organization-slug}/portal/
Your organization ID is a URL-safe identifier (e.g., acme-corp) that you chose during signup.
Organization Configuration
Configure your organization settings through the organization portal at /orgs/{orgId}/portal/.
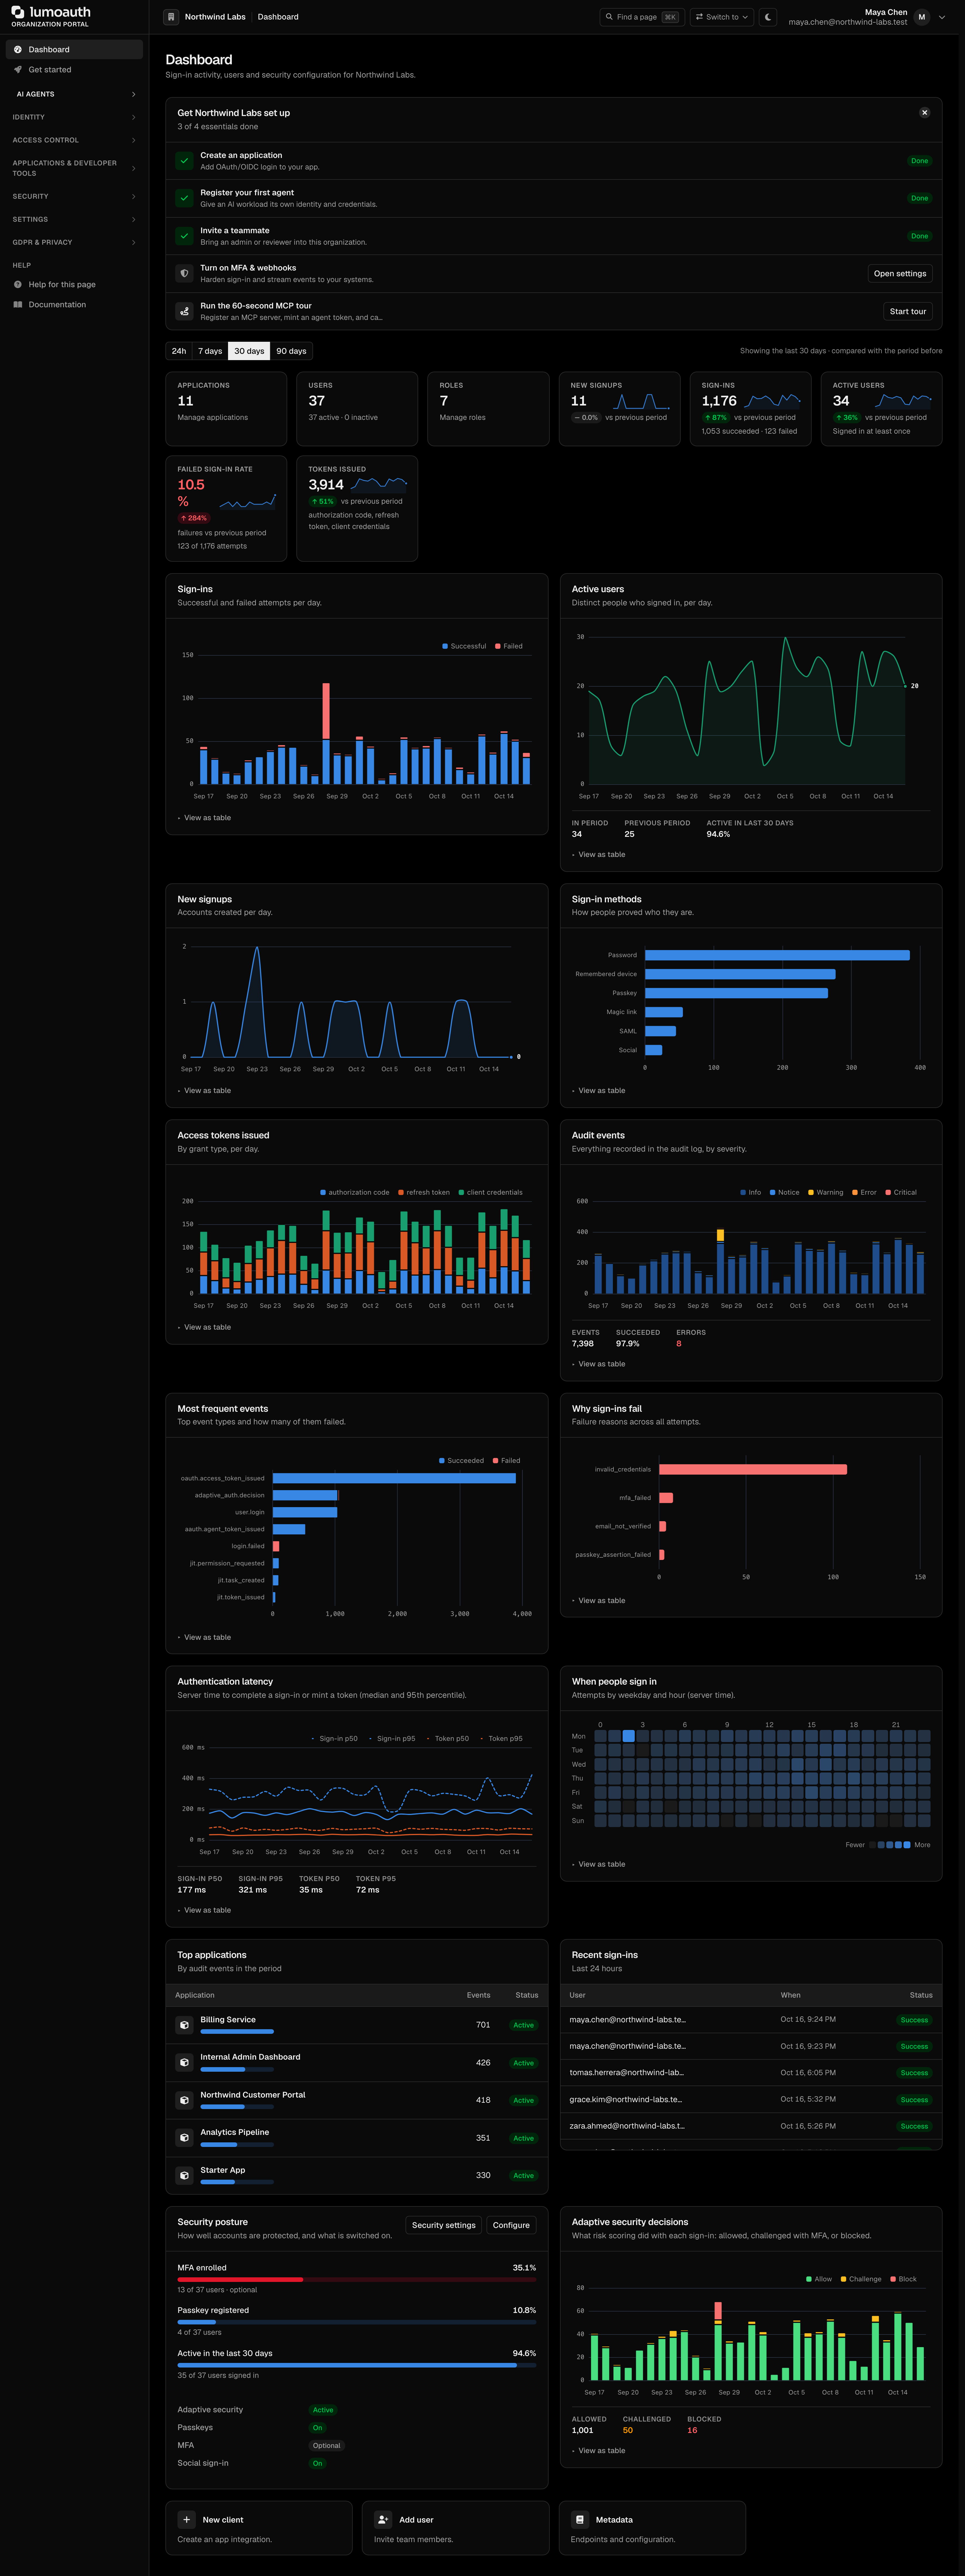
Sign-in settings
Navigate to Security → Sign-in settings (/orgs/{orgId}/portal/settings/authentication) to configure:
| Setting | Description |
|---|---|
| Identity methods | Passkeys & biometrics (including the FIDO Metadata Service check of authenticators) and Require push authentication |
| Login flow | Email-first login, magic link login |
| Password standards | Template or custom rules: minimum length and complexity requirements |
| Auth lifecycle | Session timeout, breached-password checks, password rotation |
| Platform security | OAuth security and developer-facing protocol features |
| Progressive profiling | Ask for profile details gradually across several sign-ins instead of all at registration |
| MFA policy | Off, optional, risk-based or required MFA; allowed factors, minimum strength, grace period and trusted devices (see MFA) |
| Admin API keys | Scoped keys for programmatic access to the Admin API (managed under Applications & developer tools → API keys) |
Self-registration is switched on or off with Enable self registration under Settings → Login page & emails → Login page, not on this page.
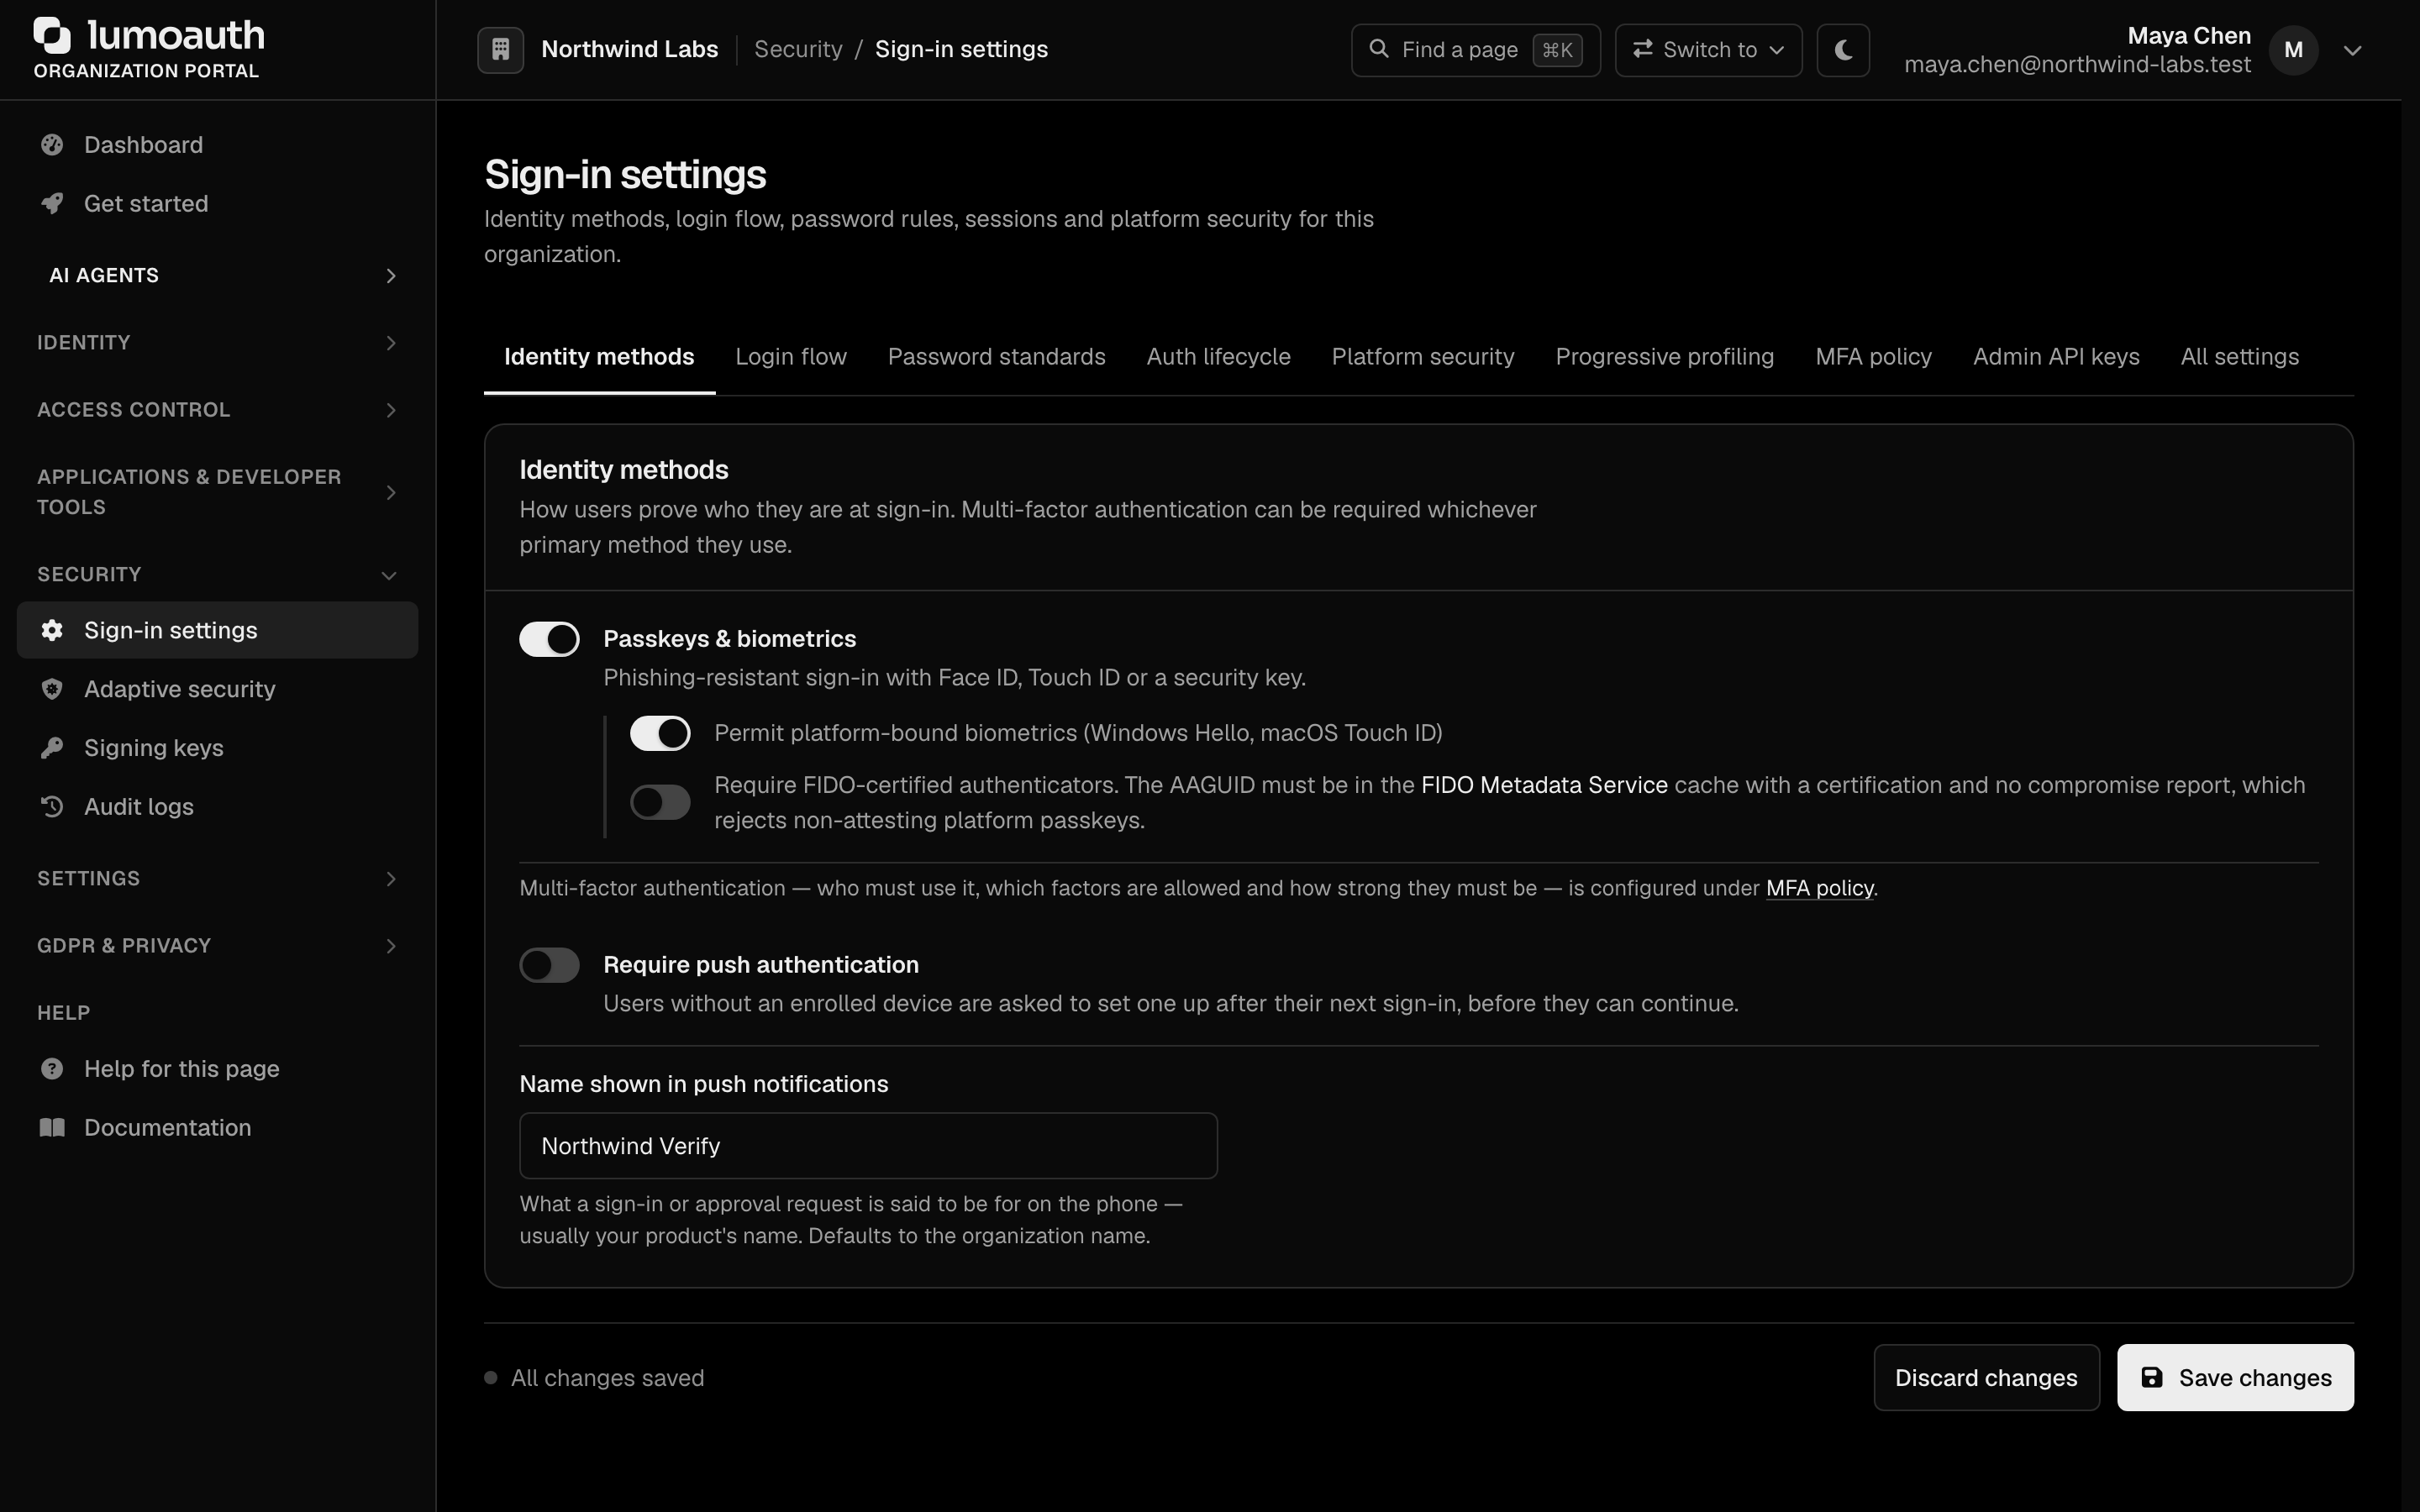
Identity Providers
Configure external identity providers for your organization:
| Provider Type | Configuration Path |
|---|---|
| Social Login | Social login section of /orgs/{orgId}/portal/integrations (Add provider) |
| SAML 2.0 IdP | Enterprise SSO (SAML) section of /orgs/{orgId}/portal/integrations, or /orgs/{orgId}/portal/saml-idps |
| OIDC Federation | Enterprise SSO (OIDC) section of /orgs/{orgId}/portal/integrations, or /orgs/{orgId}/portal/oidc-idps |
| LDAP / Active Directory | Directory sync (LDAP/AD) section of /orgs/{orgId}/portal/integrations |
All of these are under Settings → Integrations.
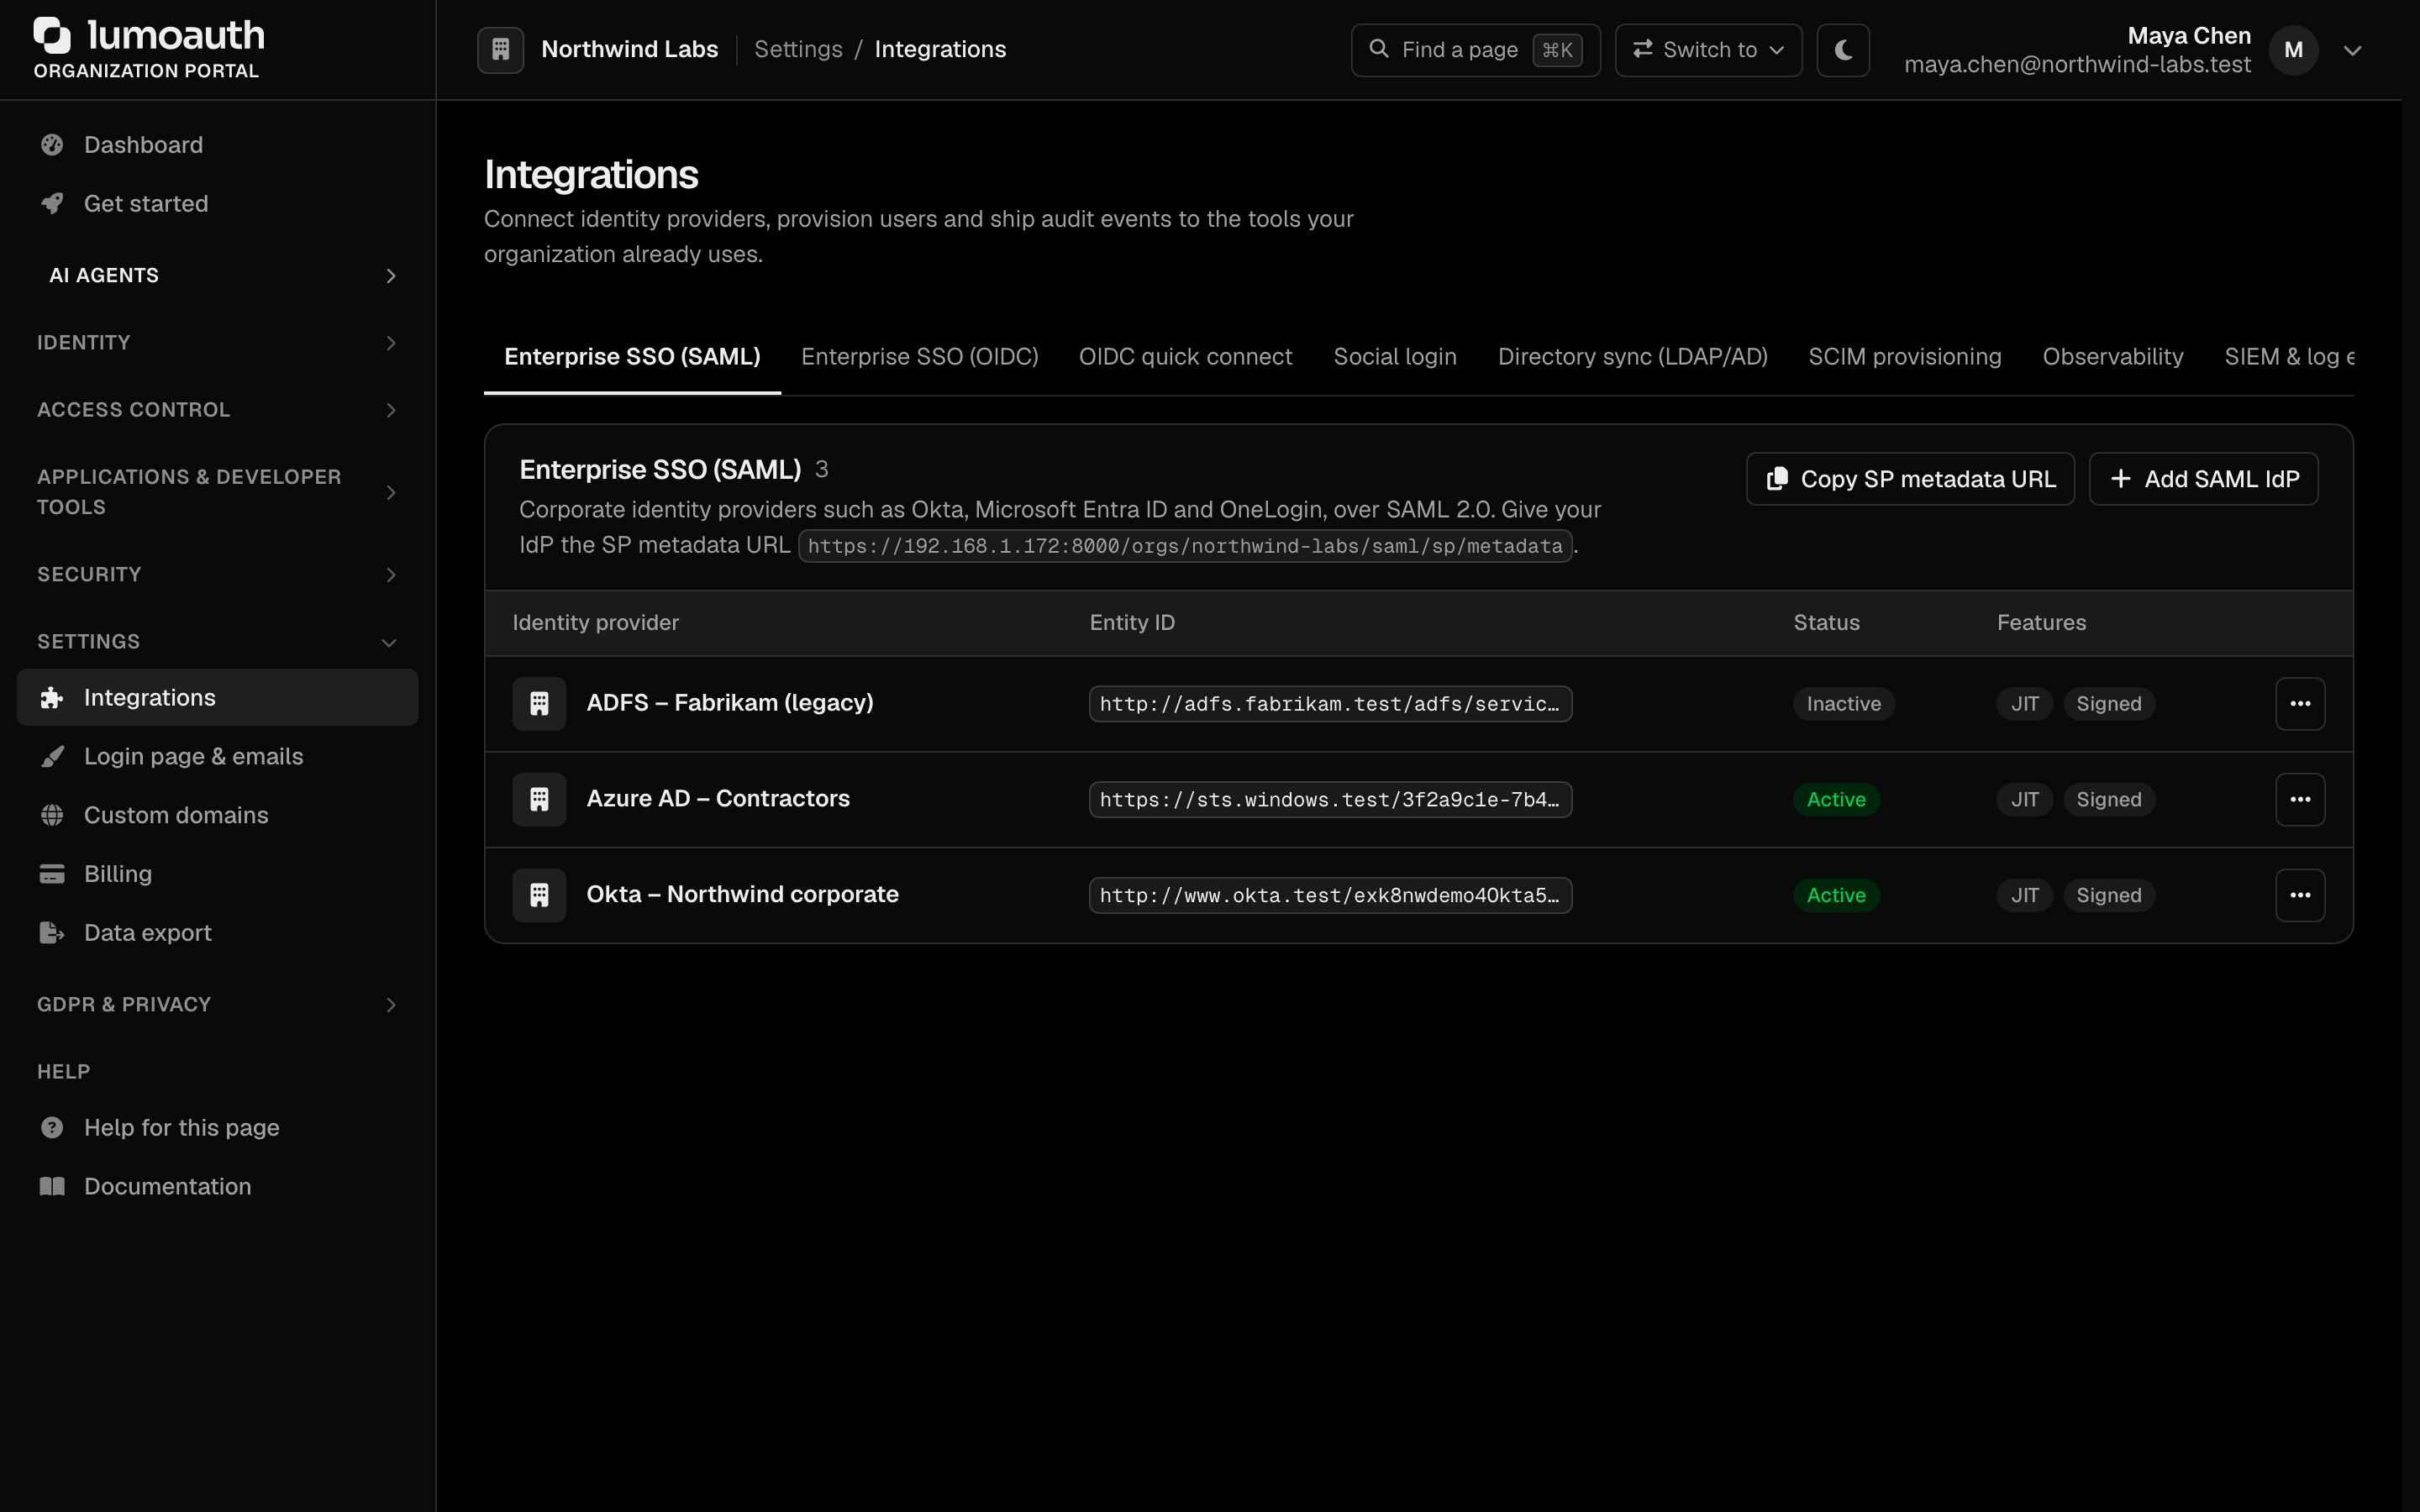
Adaptive Authentication
Configure risk-based authentication under Security → Adaptive security (/orgs/{orgId}/portal/settings/adaptive-auth):
- The adaptive security engine on/off switch
- Risk score thresholds
- Detection signals such as impossible travel, new country and IP reputation
- Network guard (Tor and datacenter/VPN blocking)
- Trusted IP ranges
See Adaptive MFA for details.
Organization Roles
Every organization starts with one system role, Tenant Admin, which holds every admin permission and cannot be deleted. Any other administrator role is one that you create under Access control → Roles & permissions (Create role). Set an access level per area, or pick Read-only, Editor or Administrator under Start from and adjust. Typical roles teams create:
| Role | Description | Typical Permissions |
|---|---|---|
| Tenant Admin (system role) | Full control over the organization | All organization operations |
| A user manager | Manage users and assignments | Create/edit/delete users, assign roles |
| An application manager | Manage OAuth and SAML applications | Create/edit/delete applications |
| An auditor | Read-only access to logs | View audit logs, view users |
See How the admin permissions work.
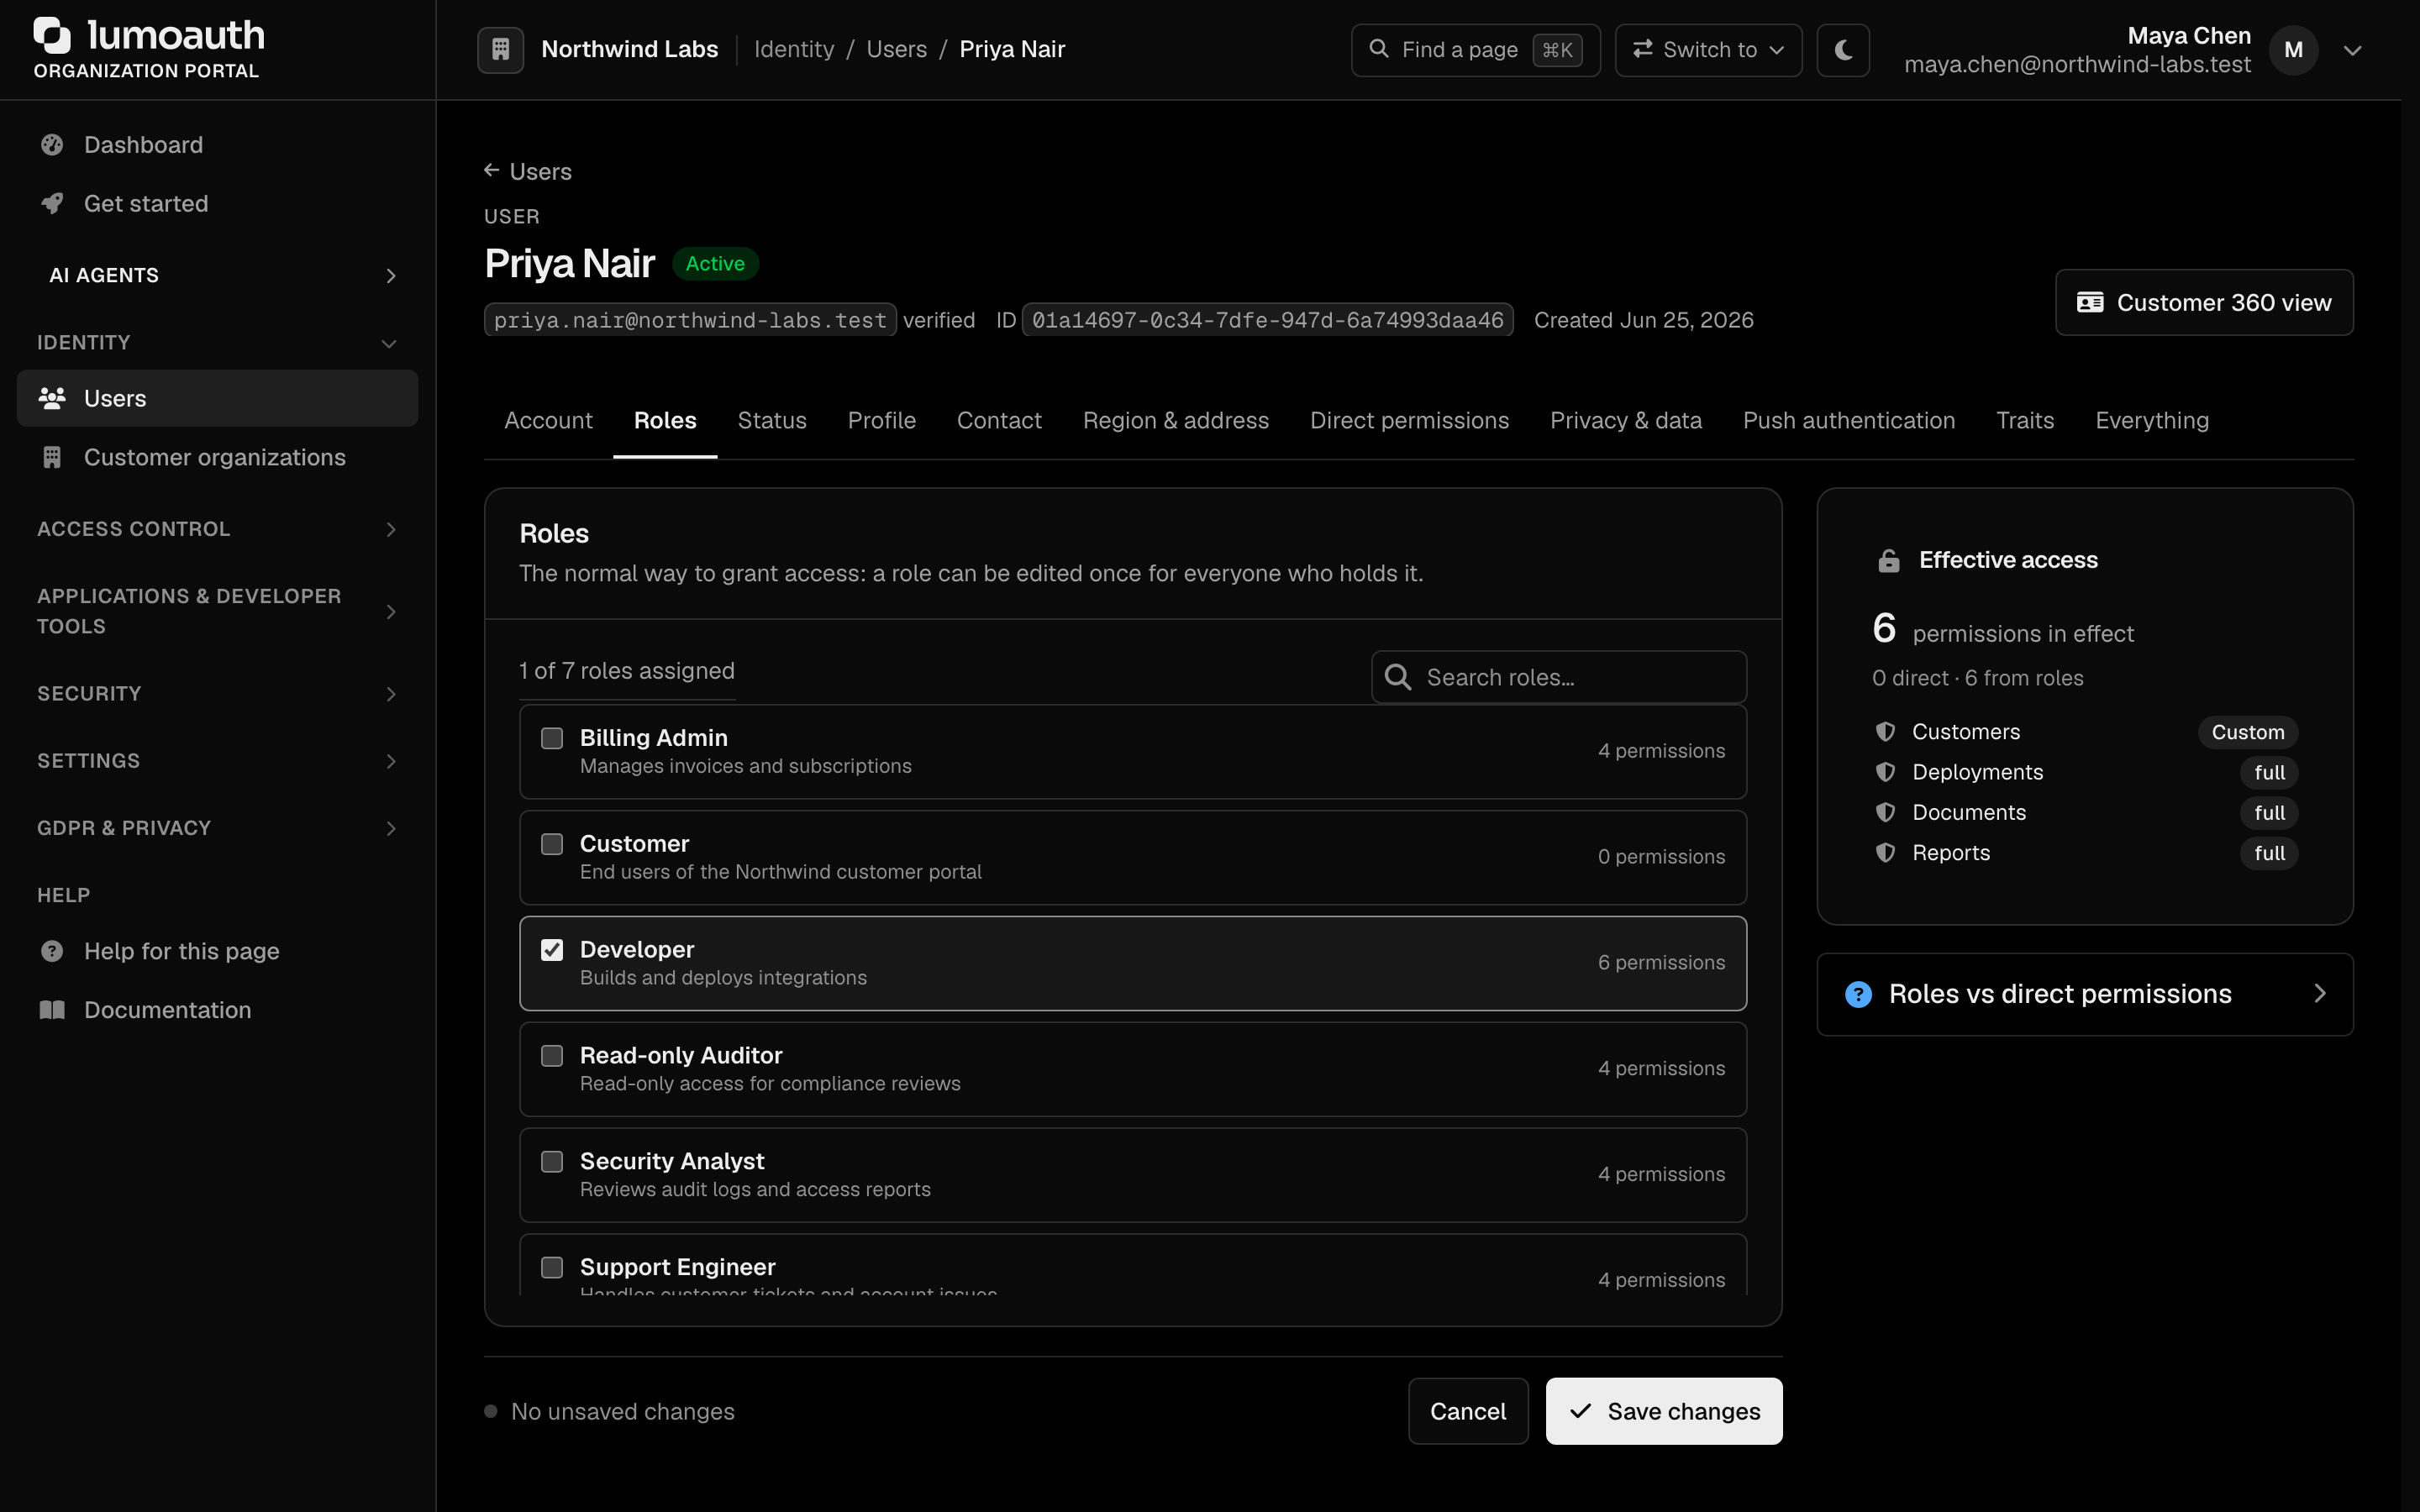
Assigning Organization Admins
- Go to Identity → Users (
/orgs/{orgId}/portal/users) - Open a user and switch to the Roles tab
- Tick the organization admin role (the system role named Tenant Admin) and click Save changes
Organization Settings via API
You can also manage organization settings from code, using the Admin API:
# Update organization authentication settings.
# Note: /api/v1/admin/settings is read-only (GET). Update each settings
# group at its own sub-resource, e.g. .../settings/authentication.
curl -X PATCH https://app.lumoauth.dev/orgs/acme-corp/api/v1/admin/settings/authentication \
  -H "Authorization: Bearer {access_token}" \
  -H "Content-Type: application/json" \
  -d '{
    "session_timeout": 1209600,
    "social_login_enabled": true
  }'
The Admin settings API is split into per-group sub-resources, each supporting GET (read) and PATCH/PUT (update):
| Group | Path |
|---|---|
| Authentication | /orgs/{orgId}/api/v1/admin/settings/authentication |
| Security | /orgs/{orgId}/api/v1/admin/settings/security |
/orgs/{orgId}/api/v1/admin/settings/email | |
| General | /orgs/{orgId}/api/v1/admin/settings/general |
GET /orgs/{orgId}/api/v1/admin/settings returns all groups in one aggregate response.
The MFA policy has its own endpoint, GET/PUT /orgs/{orgId}/api/v1/admin/policies/mfa — see the MFA API.
See the Admin API documentation for the full list of available endpoints.
Organization Data Model
Each organization owns the following resources:
Related Guides
- Organization Portal - Navigate the admin portal
- Custom Domains - Map your domain to an organization
- Your first 15 minutes in the portal - Step-by-step walkthrough of organization configuration