Observability
This section covers the observability tools available for monitoring organization health, authentication performance, and security events.
Observability Dashboard
In-portal metrics are on the Dashboard at /orgs/{orgId}/portal/ (the older /orgs/{orgId}/portal/analytics address redirects there). (The Integrations hub at /orgs/{orgId}/portal/integrations is only for configuring third-party exporters, which are covered later in this guide: log sinks such as Datadog, Axiom and Honeycomb, SCIM (automatic user provisioning), and Webhooks.)
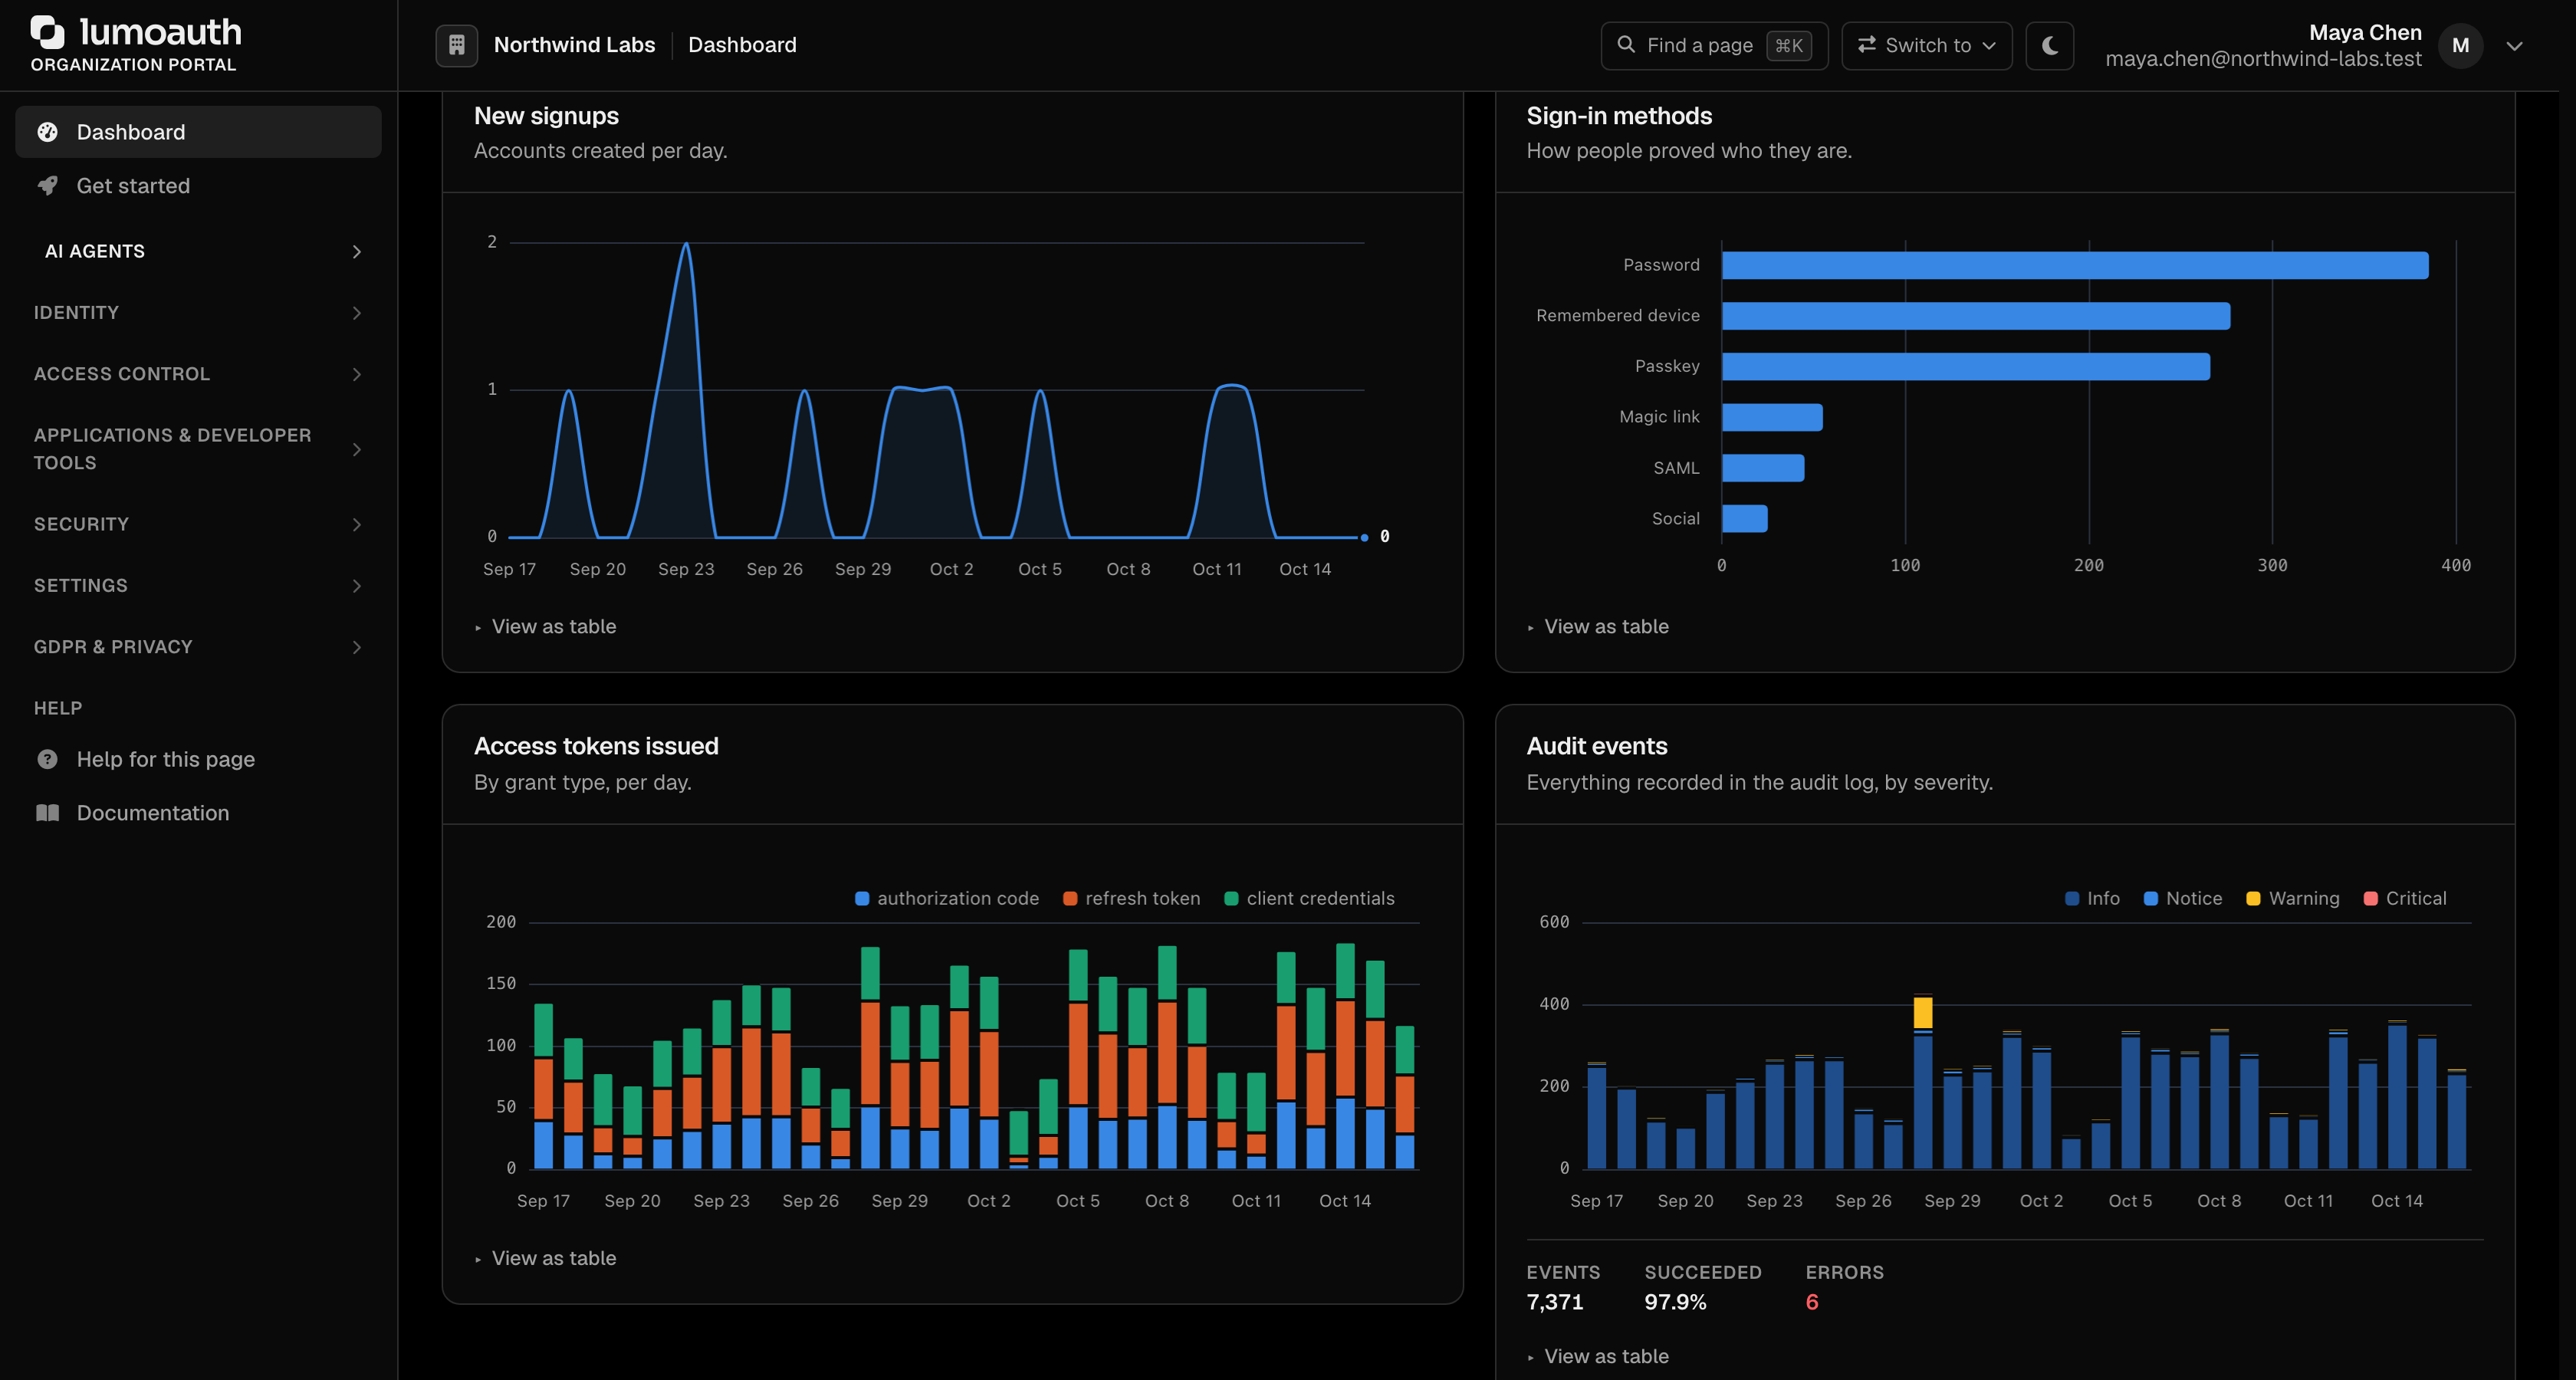
Summary tiles
| Tile | Description |
|---|---|
| Applications, Users, Roles | Counts for the organization |
| New signups | Accounts created in the period, with the change versus the previous period |
| Sign-ins | Successful sign-ins in the period |
| Active users | Distinct users who signed in |
| Failed sign-in rate | Share of sign-in attempts that failed, with the change versus the previous period |
| Tokens issued | Access tokens issued in the period |
Charts and lists
| Panel | Description |
|---|---|
| Sign-ins, Active users, New signups | Trends over the selected period against the previous one |
| Sign-in methods | Password, passkey, social, SSO, magic link and other methods as a share of sign-ins |
| Access tokens issued | Token issuance over time |
| Audit events / Most frequent events | Event volume, succeeded versus errors, and the most common event types |
| Why sign-ins fail | Failure reasons for the period |
| Authentication latency | p50 and p95 for sign-in and token requests |
| When people sign in | Sign-in attempts by weekday and hour |
| Top applications / Recent sign-ins | Most-used applications and the last 24 hours of sign-ins |
| Security posture | MFA (multi-factor authentication) enrolled, passkey registered, active in the last 30 days |
| Adaptive security decisions | Sign-ins allowed, challenged and blocked by the risk engine |
Agent activity has its own page: AI Agents → Agent activity (/orgs/{orgId}/portal/caep-dashboard) shows fleet-wide agent tasks and the shared security signals that LumoAuth has received.
Alerting
LumoAuth has no free-form alert-rule editor, but Alert channels (Settings → Integrations → Alerting & notifications) push every high- or critical-risk audit event to Slack, Microsoft Teams, PagerDuty, Opsgenie or email. For custom thresholds, use the security and authentication events that LumoAuth emits and the alerting system that you already run:
| Condition | How to alert on it |
|---|---|
| High login-failure rate | Subscribe to user.login_failed webhooks and alert in your SIEM (security information and event management system) |
| Brute force / lockout | Subscribe to user.blocked webhooks |
| Unusual activity / high risk | Forward events to Datadog/Axiom/Honeycomb (below) and alert on their query thresholds |
Brute-force lockouts and high-risk authentications are also written to the audit log and can trigger a webhook when configured.
Integration with External Tools
Export observability data and logs to your preferred monitoring stack.
Datadog, Axiom and Honeycomb
These three are log sinks, configured the same way as Splunk, Elastic, cloud storage and the other destinations:
- Go to Settings → Integrations (
/orgs/{orgId}/portal/integrations) and open the Observability area, or SIEM & log export further down. - Click Set up on the Datadog, Axiom or Honeycomb card. The form asks only for what that provider needs:
- Datadog — the Datadog site (US1, EU, US3, US5 or a custom intake URL), an API key with logs-intake permission, and optionally a service name, environment tag and extra
key:valuetags. - Axiom — the API domain (
api.axiom.counless self-hosted), the dataset and an API token with ingest permission on it. - Honeycomb — the dataset, the region (US or EU) and an ingest API key.
- Datadog — the Datadog site (US1, EU, US3, US5 or a custom intake URL), an API key with logs-intake permission, and optionally a service name, environment tag and extra
- Give the sink a Display name, switch Enable this sink on and click Create sink. Reopen the sink and click Send test event to confirm the credentials; the sink page also shows Delivered, Failed and Last success.
Secrets are stored encrypted and never shown again. Each audit event is delivered once per enabled sink, with the same PII-minimised fields as every other destination; delivery status and the last error show on the sink's row.
Earlier releases had separate Datadog, Axiom and Honeycomb pages with their own settings. Every existing integration was migrated to an equivalent log sink and the old integration switched off so nothing is sent twice. The old URLs redirect to the sink.
| Destination | Typical use |
|---|---|
| Datadog | APM + infra monitoring in one place |
| Axiom | Cost-effective log indexing at scale |
| Honeycomb | Trace-level debugging and query-based exploration |
| Other log sinks | Splunk, Elastic, Sentinel, Google SecOps, S3, OpenTelemetry and more; see SIEM & log export |
| Webhooks | Custom integrations and chat notifications (Slack, Discord, Microsoft Teams) |
Related Guides
- Audit Logs - Detailed event history
- Webhooks - Real-time event notifications
- Analytics - In-portal usage dashboards
- Adaptive MFA - Risk-based security monitoring